PROFILES
Threat Groups
From LockBit and Conti to Akira and Cl0p, anatomies of the operations behind the headlines.
Anatomies of the operations behind the headlines: how each ransomware crew works, who it hits, how it makes money, and how it ends. The catalogue below tracks close to 400 operations from live leak-site data, and the profiles go deeper on the groups that matter. Start with LockBit, Qilin and Medusa, follow live activity on the Ransomtracker, see who posted victims in the last 24 hours on ransomware attacks today, and compare operators across the year on the 2026 archive.
Start here
- LockBit 5.0: the comeback nobody wanted
- Qilin: the RaaS that ran H1 2026
- Akira: the edge-VPN ransomware
- Medusa: victims, tactics and defence
- DragonForce: the cartel that absorbed its rivals
- INC Ransom: winning by mastering the basics
Latest profiles
- Clop ransomware: victims, methods and status in 2026
 Clop ransomware has 2,339 leak-site listings and 133 confirmed attacks on record. It hit PTC Windchill in 2026, and its latest listing is from 21 October.
- Medusa ransomware: victims, tactics, and how to defend in 2026
 Medusa is a ransomware-as-a-service crew active since 2021, with 300+ claimed victims and 161 confirmed by Ransomnews. Its targets, tactics, biggest breaches and the defences that stop it.
- Interlock: the drive-by ransomware crew CISA flaggedInterlock breaks the ransomware playbook, entering through compromised websites and fake CAPTCHAs. A joint CISA-FBI advisory mapped its TTPs. Here is the profile.
- SafePay: the centralised crew that skipped affiliatesSafePay went from unknown to one of the busiest ransomware crews in under a year by ditching affiliates and hammering RDP and VPN gateways. Here is how it works.
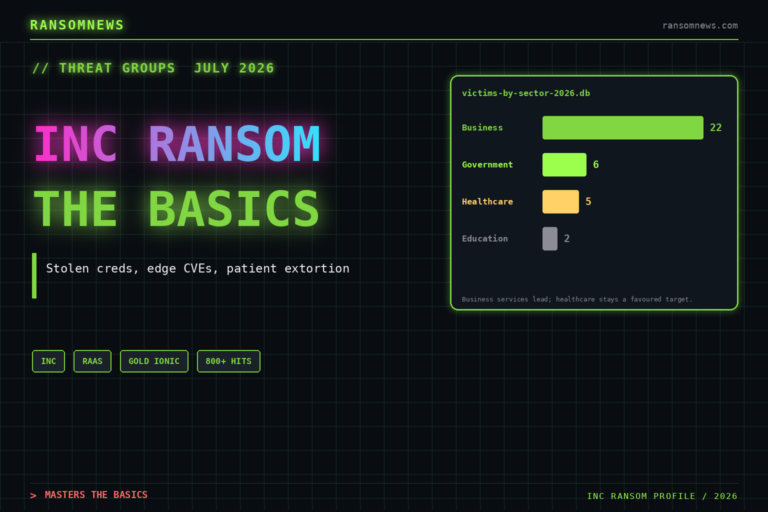
- INC Ransom: the RaaS that wins by mastering the basicsINC Ransom has claimed 800-plus victims since 2023 using stolen credentials, edge-device flaws and double extortion. Here is how the RaaS operates in 2026.
- Ransomware attribution 2026: TTPs, notes, fingerprints
 A 2026 attribution playbook for ransomware investigations, combining TTP fingerprinting against MITRE ATT&CK, ransom-note artifact analysis, leak-site monitoring, and the open-source intelligence pivots that hold up under scrutiny.
- Active Directory hardening 2026: Tier 0, DSRM, PRT theftA 2026 practitioner walkthrough of Active Directory hardening against the lateral-movement, credential-theft, and persistence techniques that modern ransomware operators rely on: Tier 0 isolation, DSRM rotation, PRT theft mitigation, and AD audit baselines.

Every ransomware group profile
Our editorial profiles of individual ransomware operations, newest first.
- Medusa ransomware: victims, tactics, and how to defend in 2026
- Interlock: the drive-by ransomware crew CISA flagged
- SafePay: the centralised crew that skipped affiliates
- INC Ransom: the RaaS that wins by mastering the basics
- Deadlock: ransomware that hides its C2 on the blockchain
- DragonForce: the cartel that absorbed its rivals
- LockBit 5.0: the comeback nobody wanted
- Akira: the edge-VPN ransomware that never slowed down
- Qilin: the RaaS that ran H1 2026 ransomware
- The Gentlemen ransomware: 483 victims and a leaked playbook
Operator interviews
The Danchev Interviews: rare on-record conversations with the people running these operations.
Tracked ransomware operators
239 ransomware operations currently profiled, accounting for 32,321 claimed victims between them. Each profile lists victims, leak-site mirror status, and first and most recent listing dates, rebuilt continuously from leak-site monitoring.