DEFENCE
Security
EDR, Zero Trust, MFA, patching, IR, what actually works against modern threats.
Defensive coverage for people who have to hold the line: the controls that actually move the needle, the vulnerabilities worth patching first, and the attacks they are meant to stop. Cornerstones include Active Directory hardening, the ransomware incident response runbook, the RDP attack landscape and SIEM vs XDR.
Check your own exposure with the free website security check and the FortiBleed checker.
Start here
- Active Directory hardening: Tier 0, DSRM, PRT theft
- Ransomware incident response runbook
- RDP attacks: ransomware’s #1 entry vector
- Detecting and responding to infostealer infections
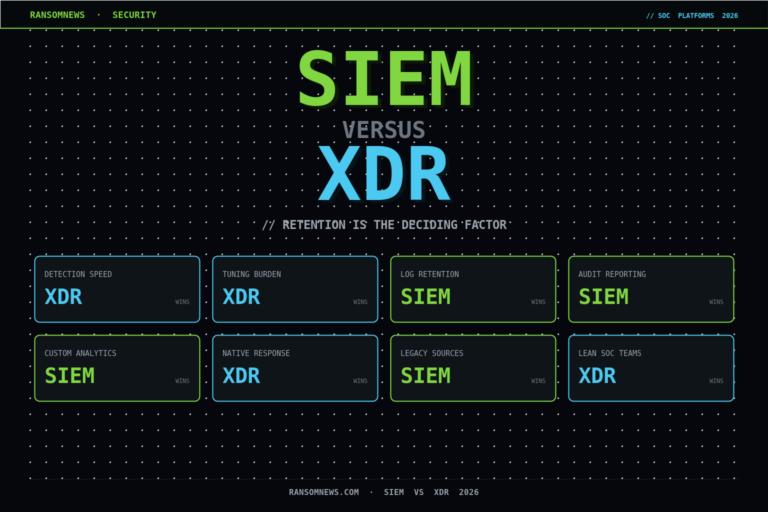
- SIEM vs XDR: retention is the deciding factor
- Cloud Exposure Index 2026: open buckets mapped
Latest security coverage
- Riemann hypothesis proof would not break encryption
 A claimed AI-assisted proof of the Riemann hypothesis is still being checked. RSA, elliptic-curve keys and Bitcoin do not depend on it. What a proof changes.
- Chase and Bank of America outage: was it a cyberattack?Chase, Bank of America, Wells Fargo and U.S. Bank customers reported outages on 16 November 2026. Chase says it is a technical issue, not a cyberattack.
- Old Bitly links hijacked in Burger King, McDonald’s and Trump tweetsBurger King and McDonald’s were not hacked. Someone re-registered the Bitly links in their 2011 tweets, and 57 of 97 links in old Trump tweets have been replaced too.
- Microsoft 365 outage: was it a cyberattack? What we knowThe Microsoft 365 outage of 12 to 13 November 2026 was not a cyberattack. Microsoft blames a network capacity upgrade. What happened and what to do now.
- CSC Telecom leak: 125 million Baltic SMS, readable in real timeAn open database at SMS provider CSC Telecom held 125 million texts from Swedbank, SEB, airBaltic and Baltic retailers, updated live. What was exposed, who has responded, and what customers and companies should do.
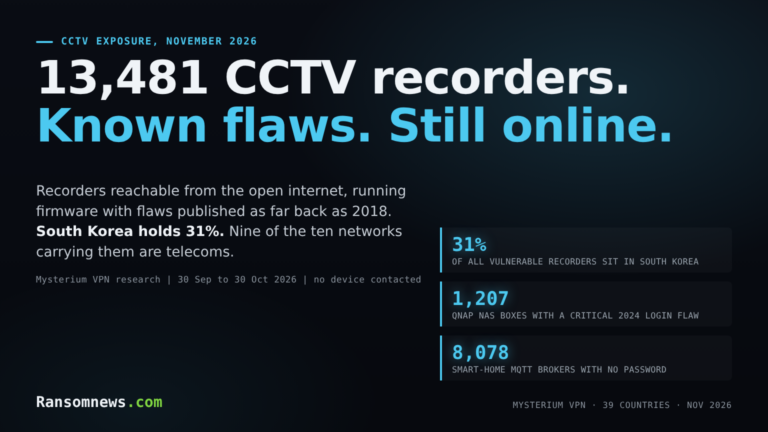
- 13,481 CCTV recorders with known flaws exposed online, 31% in South KoreaMysterium VPN counted 13,481 internet-reachable CCTV recorders running firmware with known flaws in 39 countries, 31% of them in South Korea.
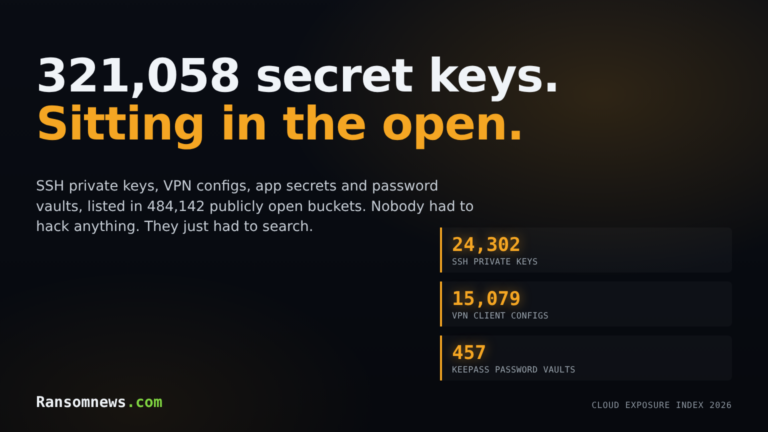
- Cloud Exposure Index 2026: 484,142 open buckets mapped484,142 publicly listable cloud buckets hold 18 billion files. Azure over-indexes on backups, and two-thirds of exposed .env secrets files were written in 2026.
- PHP2Shell: Pierluigi Paganini on the PHP flaws under attackPHP2Shell, CVE-2026-109618 and CVE-2026-109619, gives attackers remote code execution on every PHP web deployment since 5.4 and was exploited four days before the 21 October patch. Pierluigi Paganini’s Security Affairs Q&A on what operators should do, with the version, exposure and mitigation detail.
- Best VirusTotal alternatives 2026: what threat hunters run
 The VirusTotal alternatives threat hunters run in 2026: MetaDefender, ANY.RUN, CAPE, Intezer and MalwareBazaar, compared by job, upload privacy and API.
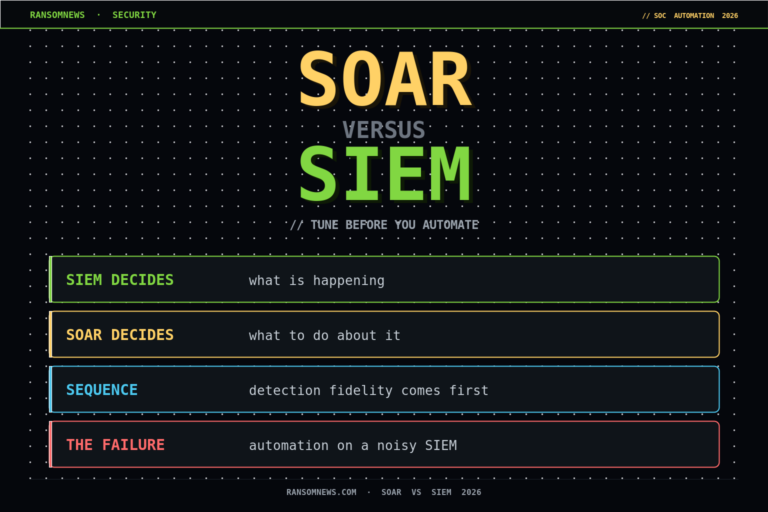
- SOAR vs SIEM 2026: tune before you automateSOAR vs SIEM in 2026: they were never alternatives. Gartner marked standalone SOAR obsolete, and the automation now ships inside your SIEM or XDR.
- SIEM vs XDR 2026: retention is the deciding factorSIEM vs XDR in 2026: XDR wins on detection speed, SIEM wins on retention and audit. Which one you can drop comes down to your compliance obligations.
- wp2shell: pre-auth RCE in WordPress core (CVE-2026-63030)wp2shell chains a REST batch-route bypass and a SQL injection into pre-auth RCE on WordPress core. WordPress shipped forced auto-updates in 7.0.2, 6.9.5 and 6.8.6.
- GodDamn ransomware blinds EDR with a Microsoft-signed driverSymantec detailed GodDamn ransomware using PoisonX, a kernel driver with a valid Microsoft signature, to terminate EDR before it encrypts.
- macOS.Gaslight: malware that prompt-injects your SOCSentinelLABS found macOS.Gaslight, a DPRK-linked Rust backdoor that embeds 38 fake system messages to make AI malware-triage agents abort. It is the first implant built to attack the analyst’s LLM, not the sandbox.
- 292 fake GitHub repos push a hash-dodging infostealerArctic Wolf found 292+ fake GitHub repositories impersonating security and fintech brands to deliver a BoryptGrab-lineage infostealer, with payloads that rotate every 60 seconds.
- 570 flaws, 2 exploited: July Patch Tuesday hits identityMicrosoft’s July 2026 Patch Tuesday fixed a record 570 flaws and three zero-days, two already exploited in AD FS and SharePoint identity infrastructure.
- The Gentlemen weaponised a Kontron driver to kill EDRThe Gentlemen ransomware weaponised a zero-day in Kontron’s ktapi.sys driver to gain kernel access and kill EDR from Microsoft, ESET, Palo Alto, and SentinelOne, researchers found.
- FortiBleed: 75,000 cracked Fortinet firewalls, no zero-day neededFortiBleed exposed cracked admin passwords for around 75,000 Fortinet firewalls across 194 countries, roughly half the internet-facing fleet. There is no new zero-day. It is config exports, weak hashing, and recycled credentials, packaged as a sales catalog.
- Registrų centras breach: 600,000 records exposedLithuania’s Centre of Registers (Registrų centras) disclosed a May 2026 breach exposing roughly 600,000 records. Attackers reused credentials of authorised institutions, queried from abroad. Alerts.bar data shows 117 stealer-log accounts tied to the agency and 60+ live infected staff endpoints across the wider Lithuanian institutional ecosystem.
- RDP attacks 2026: ransomware’s #1 entry vectorRemote Desktop Protocol remains the single most-abused initial-access vector for ransomware operators in 2026. We break down the current attack patterns (credential stuffing, broker-sold access, BlueKeep-era CVE echoes, and weaponised RDS misconfigurations) and the controls that actually move the needle.
- Alerts.bar review 2026: dark-web monitoring tested
 Alerts.bar is a continuously-updated dark-web monitoring and stealer-log intelligence platform. We’ve used it in production to power Ransomnews’s free Stealercheck tool. Here’s our independent review: features, pricing, real-world testing, and how it stacks up against HIBP, SpyCloud, Constella, and Hudson Rock.
- MSPs: ransomware’s #1 target of 2026 [Field Report]Managed service providers entered 2026 as the single highest-leverage target class in the ransomware economy. Why the channel is now the front line, which TTPs operators are running against MSPs specifically, and what the better-run shops have already changed.
- Active Directory hardening 2026: Tier 0, DSRM, PRT theftA 2026 practitioner walkthrough of Active Directory hardening against the lateral-movement, credential-theft, and persistence techniques that modern ransomware operators rely on: Tier 0 isolation, DSRM rotation, PRT theft mitigation, and AD audit baselines.
- Ransomware IR runbook 2026: NIST 800-61 r3 + CISA templatesA practitioner walkthrough of building a ransomware-specific incident response runbook in 2026, combining NIST SP 800-61 r3, CISA’s #StopRansomware playbook, and the lessons from named incidents on the Ransomtracker leak feed.
Every security article
Every article we have published in this section, newest first.
- Cloud Exposure Index 2026: 484,142 open buckets mapped
- PHP2Shell: Pierluigi Paganini on the PHP flaws under attack
- Best VirusTotal alternatives 2026: what threat hunters run
- SOAR vs SIEM 2026: tune before you automate
- SIEM vs XDR 2026: retention is the deciding factor
- wp2shell: pre-auth RCE in WordPress core (CVE-2026-63030)
- GodDamn ransomware blinds EDR with a Microsoft-signed driver
- macOS.Gaslight: malware that prompt-injects your SOC
- 292 fake GitHub repos push a hash-dodging infostealer
- 570 flaws, 2 exploited: July Patch Tuesday hits identity
- The Gentlemen weaponised a Kontron driver to kill EDR
- FortiBleed: 75,000 cracked Fortinet firewalls, no zero-day needed
- Registrų centras breach: 600,000 records exposed
- RDP attacks 2026: ransomware’s #1 entry vector
- Alerts.bar review 2026: dark-web monitoring tested
- MSPs: ransomware’s #1 target of 2026 [Field Report]
- Active Directory hardening 2026: Tier 0, DSRM, PRT theft
- Ransomware IR runbook 2026: NIST 800-61 r3 + CISA templates
- Attack-surface mapping 2026: Shodan, Censys, FOFA, Nuclei
- Detecting and responding to infostealer infections before they become breaches
- What is ransomware? A plain-English guide to how it works, who it hits and what it costs