CRIMINAL ECONOMY
Cybercrime
Ransomware operations, threat-actor profiles, breach economics, and the criminal markets that fund all of it.
The business of cybercrime: the initial-access brokers who sell the way in, the infostealer economy that feeds them, the dark-web markets where data is sold, and our own desk that tests leak claims before they become headlines. See how initial-access brokers fuel ransomware and the breach verification desk.
For live exposure data, look up any domain with Stealercheck and track active operators on the Ransomtracker.
Start here
- Initial access brokers: ransomware’s supply chain
- Breach verification desk: is the leak real?
- The week the West went after ransomware’s plumbing
- The Telegram stealer-log economy
- Exploit.in: inside a Russian hacker forum, 2005 to 2008
Latest cybercrime coverage
- n0n leaks Visa, Mastercard and JPMorgan customer data
 n0n leaked marketing data on about 16,000 JPMorgan Reserve cardholders and on Visa and Mastercard customers on 19 November 2026. All three blame suppliers.
- The Gentlemen list NVIDIA weeks after supplier JentechThe Gentlemen listed NVIDIA on 18 November 2026 with no samples. The gang named NVIDIA supplier Jentech six weeks earlier. NVIDIA has not confirmed a breach.
- Inception leaks PepsiCo staff directory, lists AMD and CignaNew extortion brand Inception named AMD, Cigna, Henry Schein, Paychex and PepsiCo on 17 November 2026. Its Cigna file holds 421,661 IT service desk tickets.
- n0n lists Eli Lilly, Visa and JPMorgan: Visa blames supplierExtortion group n0n named 59 organisations on 16 November 2026, including Eli Lilly, Visa and JPMorgan Chase. Visa says a third-party supplier was hit.
- TSMC data breach: was the chipmaker hacked? What we knowTSMC says employee data posted online came from a cloud vendor’s system, not its own. A seller wants 3 bitcoin for 46,000 records it claims to hold.
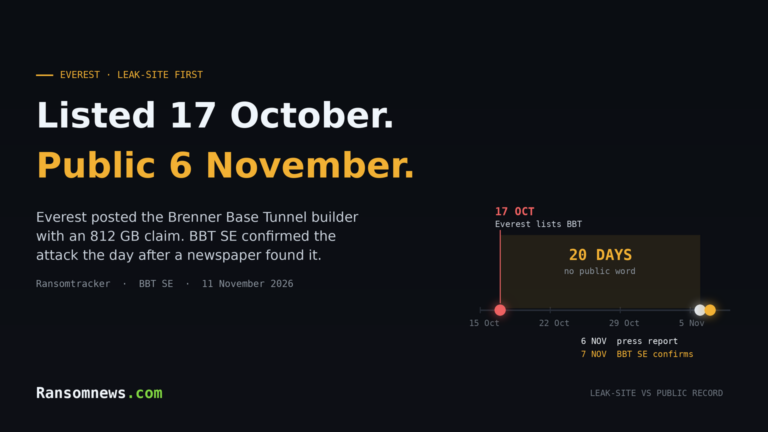
- Everest listed Brenner Base Tunnel 20 days before the newsEverest posted Brenner Base Tunnel SE on its leak site on 17 October 2026, claiming 812 GB. The tunnel builder confirmed the attack only after the press found it on 6 November.
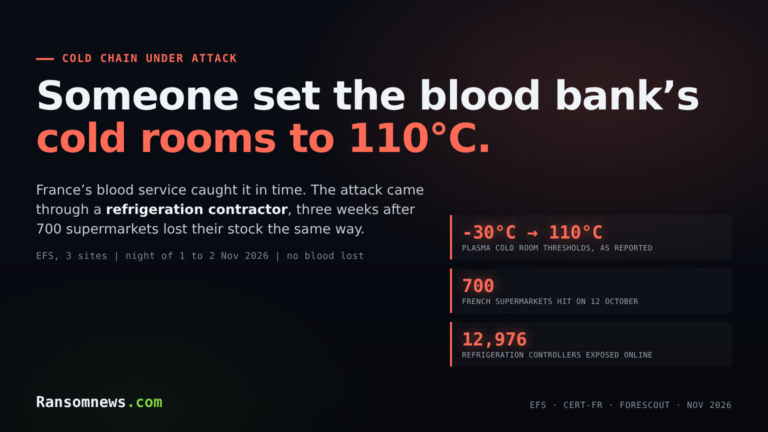
- French blood bank cyberattack: Europe’s cold-chain hack waveHackers tried to heat plasma cold rooms at France’s blood service to 110°C via a contractor. What is known about Europe’s refrigeration attack wave and who claims it.
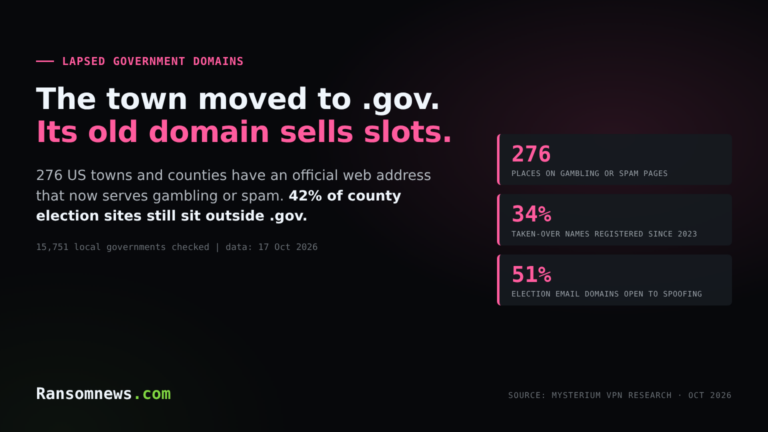
- Gambling spammers are buying lapsed US government domainsThe old official web addresses of 276 US towns and counties now serve gambling or spam, and 42% of county election sites still sit outside .gov.
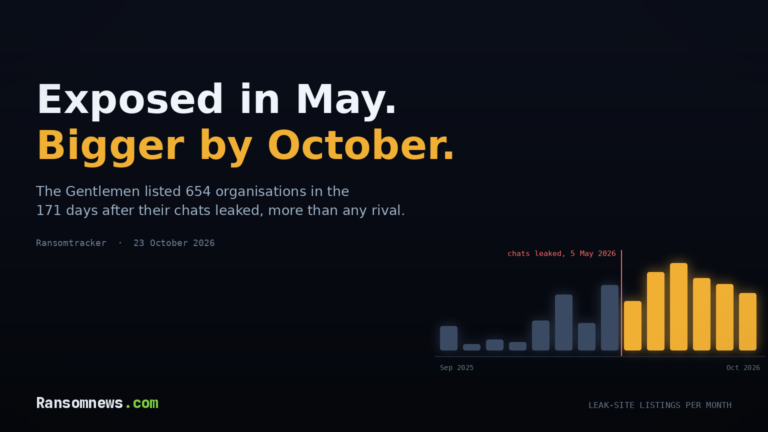
- The Gentlemen after the leak: 654 listings since MayDancho Danchev checks a copy of The Gentlemen’s leaked chats against six months of Ransomtracker data: 654 leak-site listings since 5 May 2026, more than any rival, 53 confirmed attacks, and no consequences for the crew.
- Qilin lists Joliet District 86, two years after LockBitQilin listed Joliet Public Schools District 86 on 14 October 2026, two years after LockBit claimed the same Illinois district. No data or deadline has been posted.
- RAMP admin Stallman: 10 BTC for the XSS admin’s identityRAMP’s administrator ran its escrow, bought US network access daily and offered LockBit the XSS admin’s identity for 10 BTC. Dancho Danchev reads the record.
- Rhysida lists Anne Arundel County with a 2.6 TB claimRhysida claims 2.6 TB and 814,500 files from Anne Arundel County, Maryland, including health and background-check records. The county has not responded.
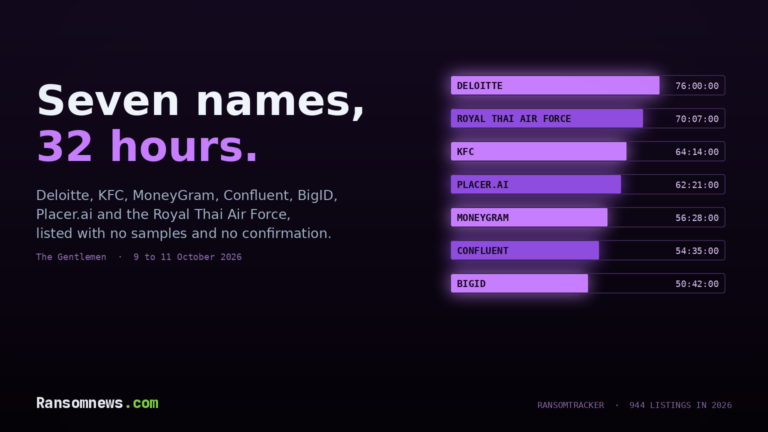
- The Gentlemen list KFC, MoneyGram, Deloitte and ConfluentThe Gentlemen ransomware group listed Deloitte, KFC, MoneyGram, Confluent, BigID, Placer.ai and the Royal Thai Air Force in 32 hours. None has confirmed a breach.
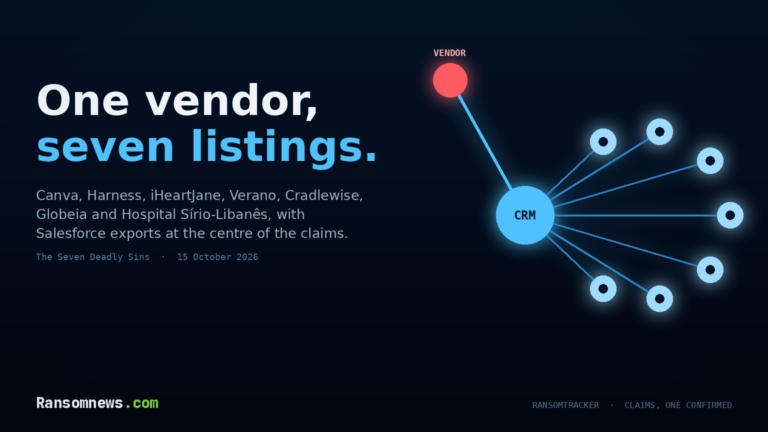
- The Seven Deadly Sins list Canva, Harness and iHeartJaneThe Seven Deadly Sins claims 230m+ rows from Canva, Harness, iHeartJane, Verano, Cradlewise, Globeia and Hospital Sírio-Libanês. Only Canva has confirmed any loss.
- n0n lists 38 ports and shipping firms in a single postExtortion group n0n listed 38 port, terminal and shipping companies in one batch on 12 October 2026, demanding $2.4m to $14m. No listed company has confirmed a breach.
- Novo Nordisk breach lawsuits: what the complaints get wrong
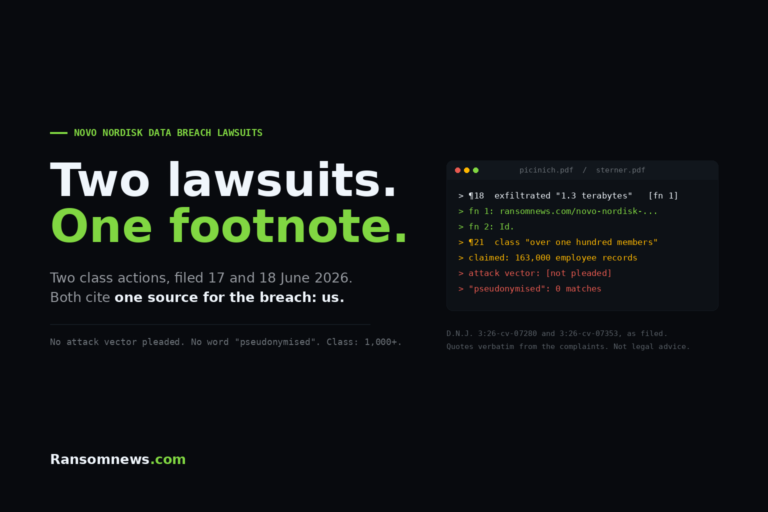
 Two class actions over the Novo Nordisk data breach cite our FulcrumSec reporting for its scale, then skip how the attackers got in and what data was exposed.
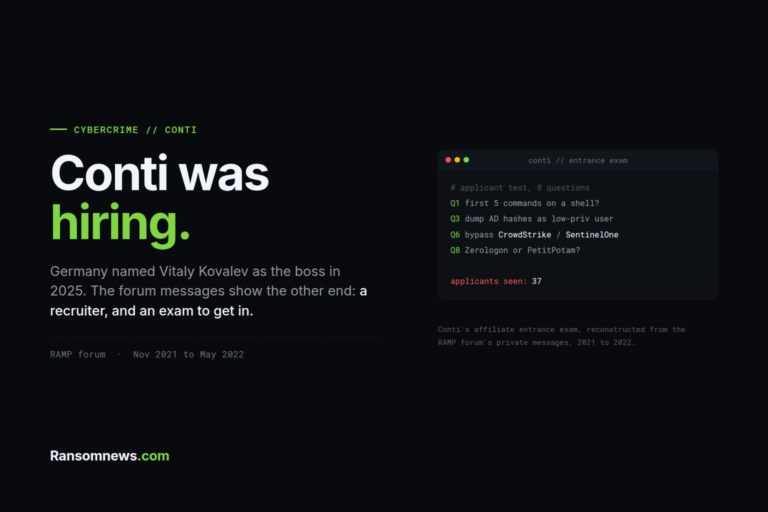
- Conti was hiring: the ransomware crew’s entrance examGermany named Vitaly Kovalev as Conti’s boss in 2025. RAMP forum messages show the other end: a recruiter, a written hacking exam, and when the hiring stopped.
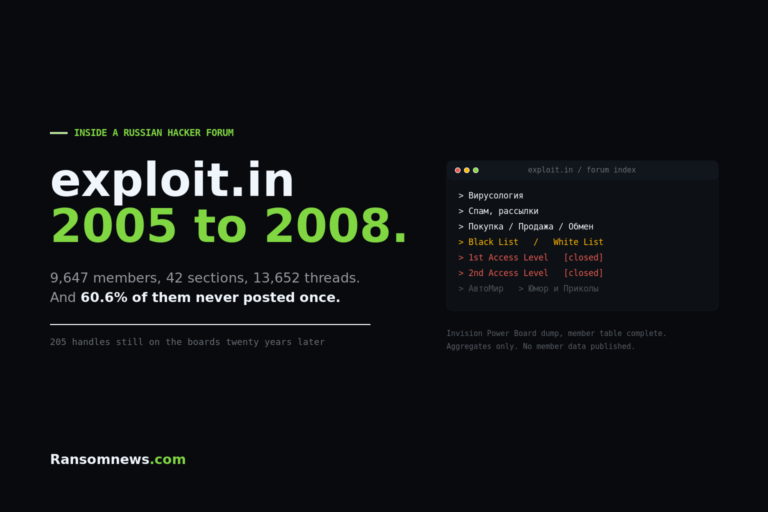
- Exploit.in: inside a Russian hacker forum, 2005 to 2008Inside the Exploit.in database, 2005 to 2008: 9,647 members of the Russian hacker forum, 60% who never posted, and 205 handles still on the boards today.
- Telegram 120M leak: we counted 63M, most from 2020A forum listing advertises 120 million Telegram records. Ransomnews parsed the 3.7GB file: 63.1 million rows, 74% Iranian, and most of it dates to 2020.
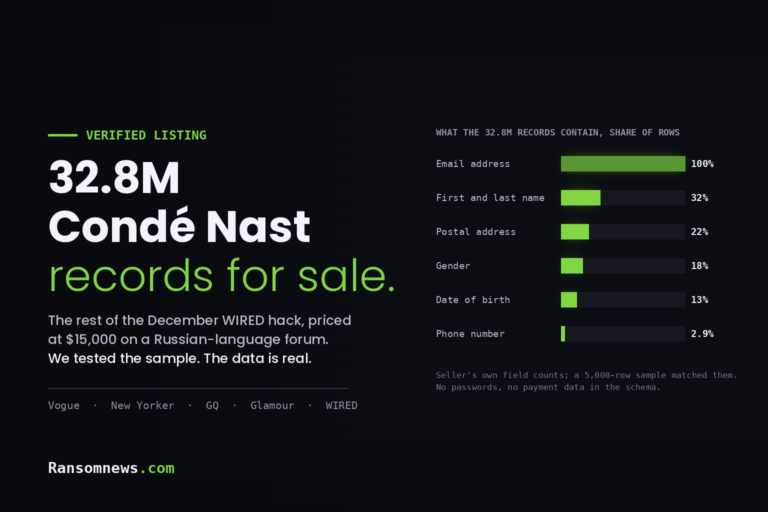
- Condé Nast: 32.8M user records for sale, sample verifiedA 32.8M-record Condé Nast user database is on sale for $15,000 on a Russian-language hacker forum. We tested the sample: genuine account data, and the rest of the December WIRED hack.
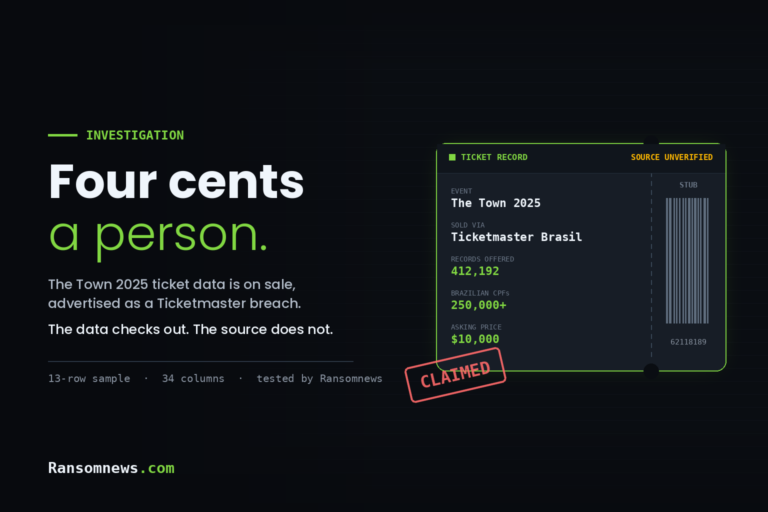
- The Town 2025 ticketing data sold as a Ticketmaster breachA seller is offering 412,192 Latin American ticket-buyer records from The Town 2025, including 250,000 Brazilian CPFs, at about four cents a head. We tested the sample.
- Micro-Comm hack is separate from the US water attacksThe FBI water-sector PLC alert and the Barracuda ransomware breach at supplier Micro-Comm landed a day apart. The evidence says they are not the same story.
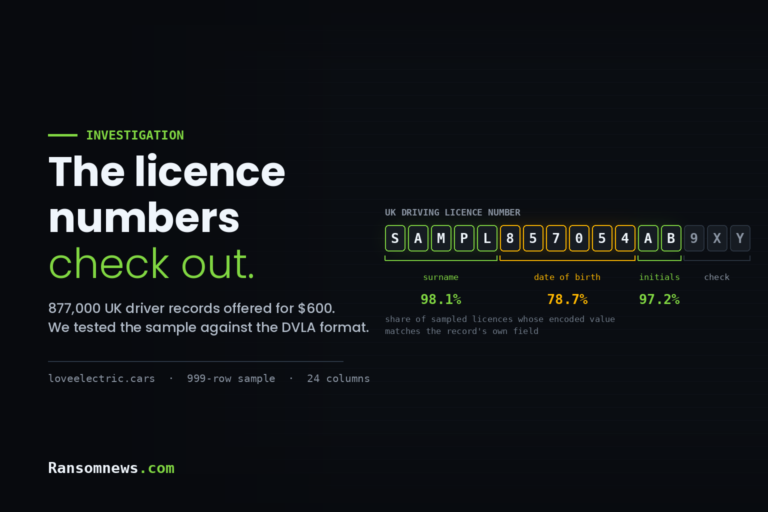
- Love Electric driver data for sale: NI, licence numbersA seller is offering 877,000 driver records from UK EV salary sacrifice broker Love Electric, including National Insurance and driving licence numbers. We checked the sample.
- Live Stripe keys for 659 merchants, published for freeStripe was not breached. A forum dataset holds live API keys for 659 of its merchants, plus 35GB pulled from them. We told Stripe before publishing this.

Every cybercrime article
Every article we have published in this section, newest first.
- The Gentlemen after the leak: 654 listings since May
- Qilin lists Joliet District 86, two years after LockBit
- RAMP admin Stallman: 10 BTC for the XSS admin’s identity
- Rhysida lists Anne Arundel County with a 2.6 TB claim
- The Gentlemen list KFC, MoneyGram, Deloitte and Confluent
- The Seven Deadly Sins list Canva, Harness and iHeartJane
- n0n lists 38 ports and shipping firms in a single post
- Novo Nordisk breach lawsuits: what the complaints get wrong
- Conti was hiring: the ransomware crew’s entrance exam
- Exploit.in: inside a Russian hacker forum, 2005 to 2008
- Telegram 120M leak: we counted 63M, most from 2020
- Condé Nast: 32.8M user records for sale, sample verified
- The Town 2025 ticketing data sold as a Ticketmaster breach
- Micro-Comm hack is separate from the US water attacks
- Love Electric driver data for sale: NI, licence numbers
- Live Stripe keys for 659 merchants, published for free
- Verified.ru: inside the archive of a cybercrime bureaucracy
- McDonald’s employee data listed for sale in wider Entra campaign
- 7.3M chess.com records leaked, and the data is real
- Quake3 and morgot: tracing REvil’s source-code developer
- Pokémon Center vending ‘breach’ is old 2016 data
- Israeli population registry for sale, but the data is old
- Żabka confirms breach via supplier account, data for sale
- 5socks.net: 20 years of proxy crime, 2004 to seizure
- Deadlock: ransomware that hides its C2 on the blockchain
- Clover Health discloses social-engineering breach in 8-K
- DragonForce: the cartel that absorbed its rivals
- ShinyHunters’ Salesforce extortion wave hits Fluke, Ingram
- LockBit 5.0: the comeback nobody wanted
- Deutsche Bank breached via supplier as Unsafe gang leaks data
- Scattered Spider duo jailed 5.5 years over £29M TfL hack
- World Leaks dumps 19,000 files tied to India nuclear plant
- Akira: the edge-VPN ransomware that never slowed down
- Coca-Cola’s Fairlife halts US production after ransomware
- Qilin: the RaaS that ran H1 2026 ransomware
- The week the West went after ransomware’s plumbing
- Anubis ransomware is exploiting Citrix Bleed 2 for access
- Kairos took $1M from a US government body and encrypted nothing
- XSS forum: from DaMaGeLaB to the 2025 takedown
- 1.16 billion attacks: how the FortiBleed crew broke FortiGate
- FortiBleed: exposed firewalls are a ransomware early warning
- Novo Nordisk hit by FulcrumSec: the stealer logs saw it coming
- The Gentlemen ransomware: 483 victims and a leaked playbook
- Ransomware runs office hours: what 16,699 leak posts reveal
- 62% of database ransom wallets were never paid
- Ransomware ditched encryption in May 2026: here’s why
- Initial Access Brokers 2026: ransomware’s supply chain
- The Telegram stealer-log economy: how stolen credentials are sold
- How stealer logs power modern ransomware attacks