A 2026 attribution playbook for ransomware investigations, combining TTP fingerprinting against MITRE ATT&CK, ransom-note artifact analysis, leak-site monitoring, and the open-source intelligence pivots that hold up under scrutiny.
Jesse William McGraw
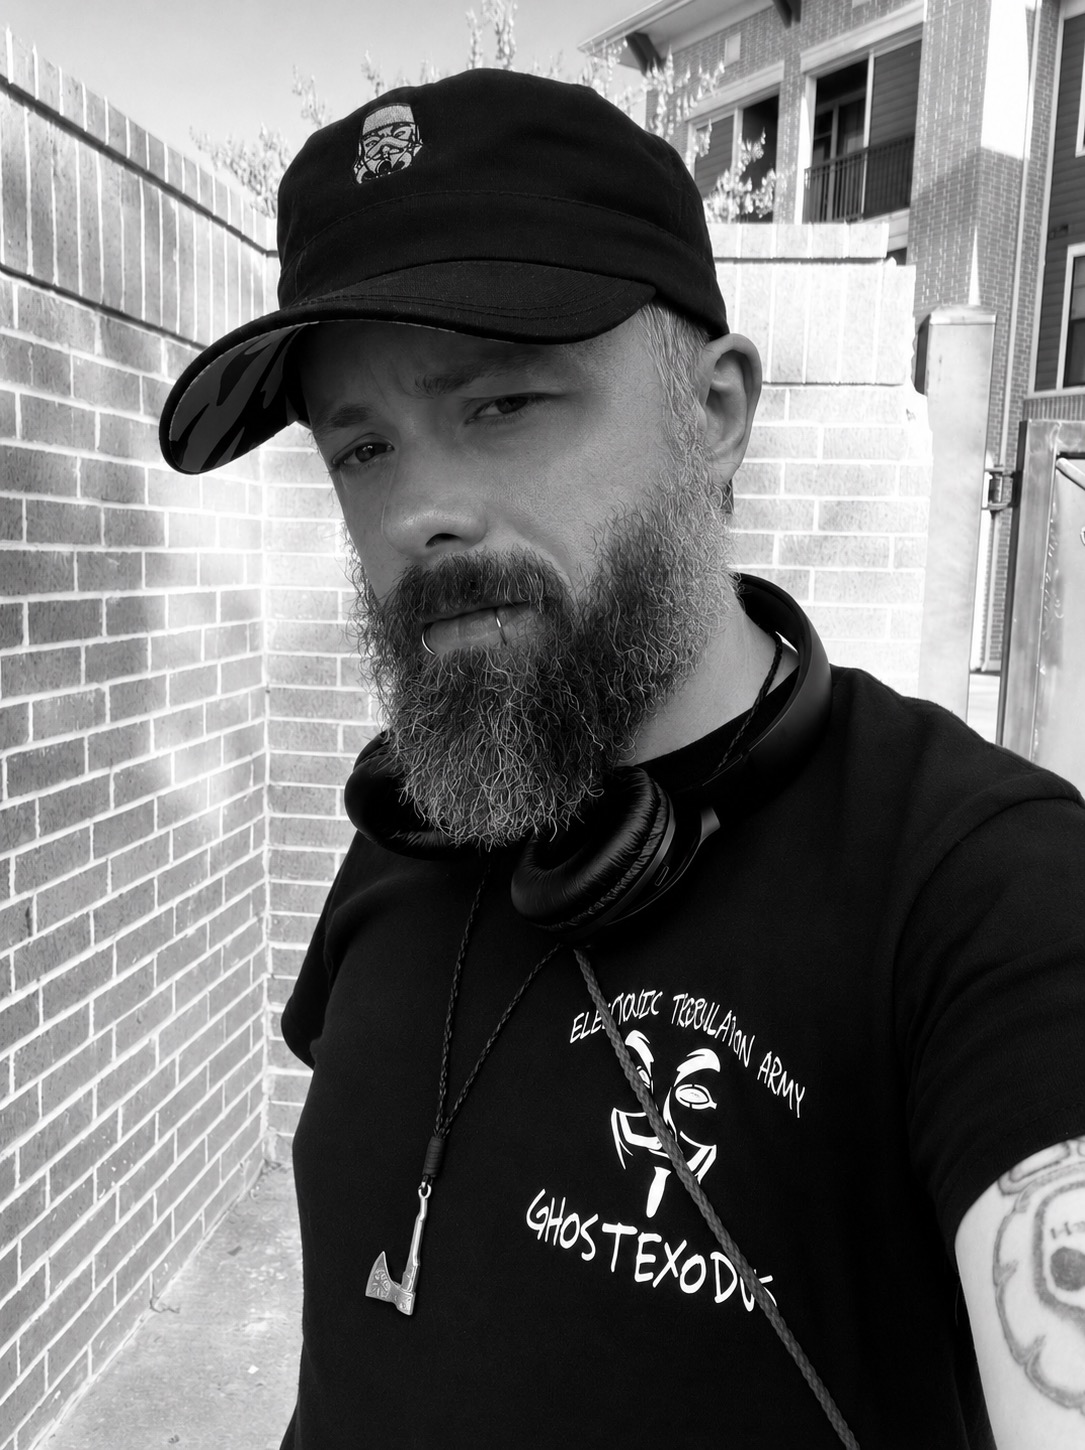
Jesse William McGraw
Jesse William McGraw, also known as GhostExodus, is a former insider threat and threat actor. He became the first person in recent U.S. history to be convicted of corrupting industrial control systems. Today he focuses on threat intelligence, OSINT, and public speaking, using his knowledge to bring awareness to the security risks that organisations and individuals face.
A 2026 practitioner walkthrough of Active Directory hardening against the lateral-movement, credential-theft, and persistence techniques that modern ransomware operators rely on: Tier 0 isolation, DSRM rotation, PRT theft mitigation, and AD audit baselines.
A 2026 self-doxxing tutorial: run the same OSINT tools attackers use, on yourself, to find every account, leaked credential, and broker entry tied to your identity. With remediation steps for each finding.
An executive-level explainer of double extortion (the dominant ransomware playbook in 2026) covering how it works, why backups don’t fully defeat it, and the policy choices boards now have to make in the first hour of an incident.
A practitioner’s step-by-step tutorial for hardware-key MFA in 2026. Which YubiKey to buy, how to enroll it on Google, Microsoft, GitHub, AWS, and your password manager, plus the recovery-key gotcha that locks people out.
A practical 2026 walkthrough for removing your name, address, and phone from the major data broker sites, using DeleteMe, Optery, and the manual fallback for the holdouts.
A practitioner’s deep-dive on OSINT.industries: what it returns for username and email queries, how I use it for journalism and due diligence, and the ethics framework I won’t run a query without.
A practitioner’s tutorial for investigating a suspicious URL safely: fingerprinting the kit, attributing it to a campaign, and reporting it to takedown services. Real tools, step-by-step, no enterprise budget required.
A step-by-step tutorial for building a free malware analysis sandbox at home: Windows reverse-engineering with FlareVM, Linux analysis with REMnux, and automated detonation with Cuckoo.
A practitioner’s tutorial for assembling a working threat-actor profile from public sources: MITRE ATT&CK for TTPs, Mandiant and CrowdStrike for attribution context, Malpedia for malware lineage, plus a clean note-taking template.