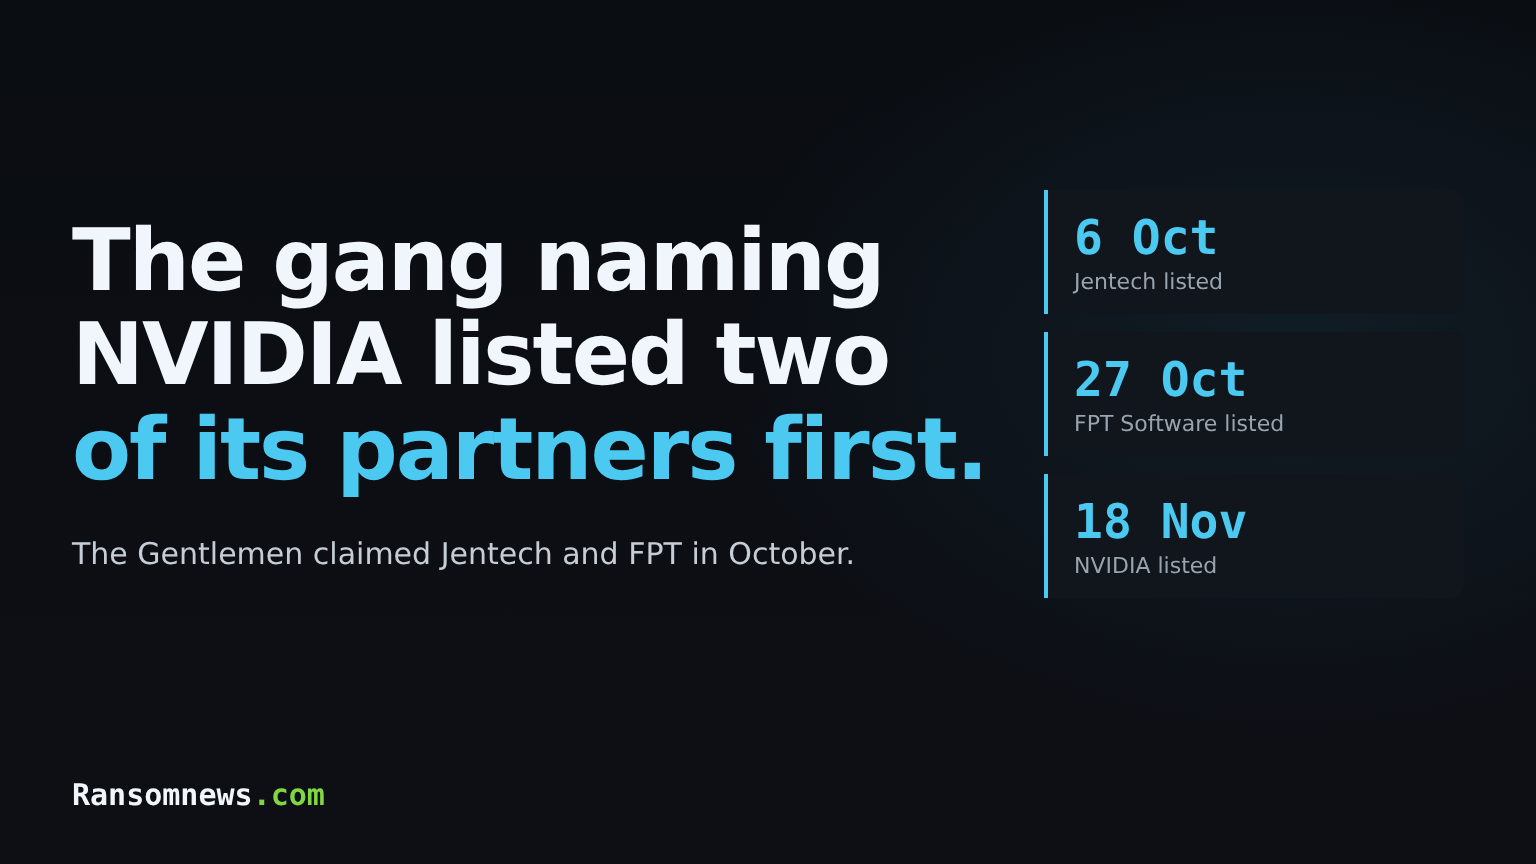
The Gentlemen ransomware group listed NVIDIA on its leak site on 18 November 2026, with no sample files and a countdown that runs out on 28 November. NVIDIA has not confirmed a breach. The same site already lists two companies that work with the chipmaker: heat-spreader supplier Jentech Precision Industrial, named on 6 October, and IT services firm FPT Software, named on 27 October.
In brief
- The claim: NVIDIA appeared on The Gentlemen’s leak site on 18 November 2026. The entry has no samples, no file list and no data volume.
- The deadline: a countdown on the entry runs out on the morning of 28 November, UTC.
- NVIDIA’s position: the company has not confirmed a breach, and Ransomnews found no public statement about the listing.
- The partners: the gang listed NVIDIA supplier Jentech on 6 October, claiming more than 9TB of data, and FPT Software on 27 October.
- The contact: the negotiation ID on the NVIDIA entry matches one that Check Point Research attributed to the group’s administrator.
- The record: The Gentlemen have posted 1,107 listings in 2026. Ransomnews has confirmed 91 attacks by the group this year from public sources.
What did The Gentlemen post about NVIDIA?
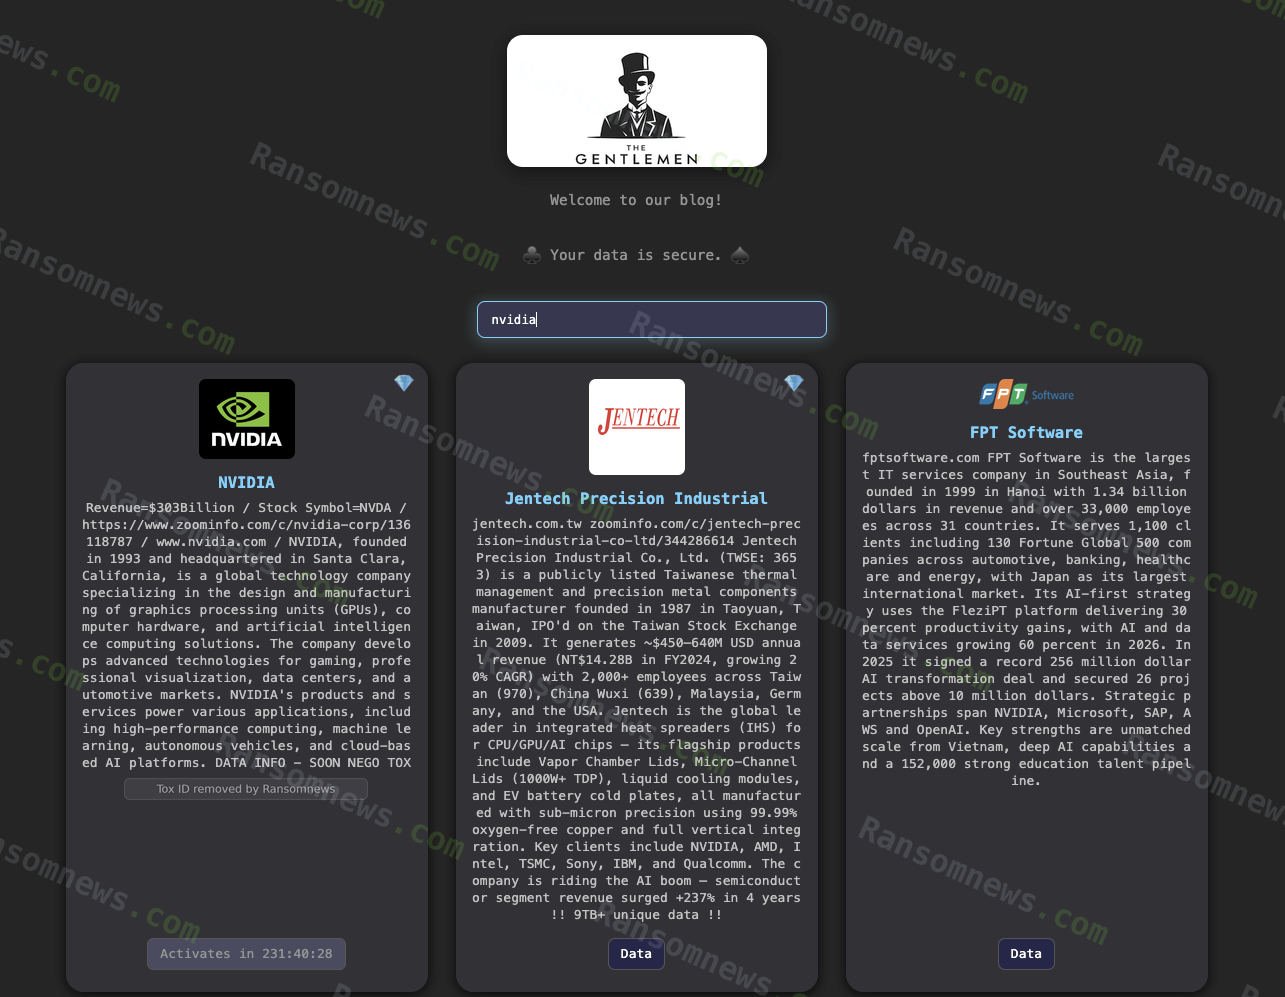
The Ransomtracker recorded the NVIDIA entry at 08:48 UTC on 18 November 2026. It shows the company’s logo, its stock ticker, a revenue figure of $303 billion, a link to a business-directory profile and a short company description. Under that, the entry says information about the data is coming “soon” and gives a Tox messenger ID for negotiations. It names no files, shows no samples and states no volume.
Where older entries show a “Data” button, NVIDIA’s shows a countdown. It stood at just under 232 hours when Ransomnews captured the page on 18 November, which puts the gang’s publication time on the morning of 28 November, UTC.
The Ransomtracker logged the entry less than 12 hours after NVIDIA reported its third-quarter results, which the company scheduled for about 21:20 UTC on 17 November. NVIDIA has not confirmed a breach, and Ransomnews found no public statement from the company about the listing as of 18 November. Aras Nazarovas, a researcher at Cybernews, expects the claim to be “either misattributed data, or a small, relatively inconsequential breach”, Technext24 reported.
Which NVIDIA partners are on the same leak site?
A search for “nvidia” on the gang’s site returns three entries, and the Ransomtracker holds a timestamp for each.
| Organisation | Listed (UTC) | Tie to NVIDIA | What the entry shows |
|---|---|---|---|
| Jentech Precision Industrial | 6 October 2026, 21:00 | Supplies heat spreaders and cooling parts for NVIDIA’s AI chips | Claims “9TB+” of data and shows a “Data” button |
| FPT Software | 27 October 2026, 07:24 | Parent company FPT has been an NVIDIA partner since April 2024 | States no volume and shows a “Data” button |
| NVIDIA | 18 November 2026, 08:48 | The chipmaker itself | No samples or volume, and a countdown to 28 November |
Jentech is a Taiwan-listed maker of heat spreaders, the metal lids that sit on top of processors, and of liquid-cooling parts. The Taipei Times reported in July on its heat spreader design for NVIDIA’s Vera Rubin platform, and Jentech describes itself as an NVIDIA MGX ecosystem partner. It was one of 33 organisations the Ransomtracker logged from The Gentlemen on 6 October. The gang’s entry lists NVIDIA, AMD, Intel and TSMC among Jentech’s clients.
FPT Software is the IT services arm of Vietnam’s FPT Corporation, which announced a partnership with NVIDIA in April 2024 that included a planned $200 million AI factory. The gang’s entry names NVIDIA among FPT Software’s partners.
Neither company has confirmed an incident that Ransomnews could find. Dark Web Intelligence noted on 27 October that FPT Software had not commented. Ransomnews has not opened or downloaded either data set.
The three entries do not show where any NVIDIA files came from. They show that the group claimed a company inside NVIDIA’s hardware supply chain six weeks before it named NVIDIA. A supplier’s files can include its customers’ drawings, specifications and correspondence, so the first sample the gang publishes should show whether the material comes from NVIDIA’s own network or from a partner’s.
Who is behind the negotiation contact on the NVIDIA entry?
Ransomnews compared the Tox ID on the NVIDIA entry with the IDs Check Point Research published in May 2026, after The Gentlemen’s internal database leaked. It is an exact match for the ID Check Point attributed to the programme’s administrator, who uses the handles zeta88 and hastalamuerte.
Free tool
How does your own site score?
Run the same forty passive checks against your own domain: TLS and certificates, security headers, SPF and DMARC, cookies before consent, and what your stack quietly reveals. A grade out of 100 in about fifteen seconds.
No signup. Nothing installed. We only request what your site already serves publicly.
Check Point found eight Tox IDs across the group’s campaigns and tied the administrator’s to four of them, which it read as evidence that the administrator runs some intrusions personally. The same report says this ID is displayed on the leak site as a contact for affiliates and victims. The match shows that talks over the NVIDIA entry would run through the core of the operation. It does not show who carried out any intrusion. Ransomnews is not publishing the ID.
How often are The Gentlemen’s claims confirmed?
The Gentlemen have posted 1,107 listings in 2026, according to the Ransomtracker, second only to Qilin‘s 1,192. Ransomnews has verified 95 attacks by the group against a public source such as a breach notification or regulatory filing, 91 of them this year. That is about one confirmed attack for every twelve listings.
The group has named large companies before. Between 9 and 11 October it listed Deloitte, KFC, MoneyGram and Confluent with three other organisations, and none of the seven is in the confirmed dataset as of 18 November.
NVIDIA has confirmed an attack before. In March 2022 the company said an intruder had taken employee credentials and proprietary information, after the Lapsus$ group claimed 1TB of its data. NVIDIA learned of that intrusion on 23 February 2022 and confirmed the theft six days later.
Who are The Gentlemen?
The Gentlemen is a ransomware-as-a-service operation that posted its first leak-site entry in September 2025. Affiliates break in, steal data and encrypt systems, and the group publishes the files of victims who do not pay, a model known as double extortion. Ransomnews profiled the group in June and has covered its activity after the May leak and the driver flaw it used to switch off endpoint security tools.
What would confirm or disprove the claim?
- Samples or a file list. Folder names, document templates and email domains show whose network a set of files came from.
- A statement from NVIDIA. US-listed companies must report a material cybersecurity incident to the SEC on Form 8-K within four business days of deciding that it is material.
- Statements from Jentech or FPT Software. Neither has said whether it was attacked or what customer material it held.
- The countdown. It runs out on the morning of 28 November, UTC.
What should NVIDIA staff, suppliers and partners do?
- NVIDIA staff: expect phishing that uses the claim, such as fake security notices and password-reset requests. Report them, and do not sign in through a link in an email.
- Suppliers and partners: check which NVIDIA drawings, specifications and credentials you hold and who can reach them. Check Point’s reading of the leaked chats describes entry through exposed VPNs and management interfaces, and our June profile found victims with staff logins already in stealer logs. Stealercheck shows whether a domain appears in them.
- NVIDIA customers: the entry names no customer data. There is nothing to act on unless NVIDIA says otherwise.
Frequently asked questions
Was NVIDIA hacked by The Gentlemen?
NVIDIA has not confirmed a breach. The Gentlemen listed the company on 18 November 2026 without samples, a file list or a data volume. The entry is the gang’s claim, and the same leak site holds earlier entries for NVIDIA supplier Jentech and for FPT Software.
When do The Gentlemen say they will publish NVIDIA data?
The countdown on the entry runs out on the morning of 28 November 2026, UTC. It stood at just under 232 hours when Ransomnews captured the page on 18 November.
What data do The Gentlemen claim to have from NVIDIA?
The entry does not say. It promises information “soon” and shows no samples, file names or volume.
Is Jentech an NVIDIA supplier, and was it attacked?
Jentech Precision Industrial makes heat spreaders and cooling parts used with NVIDIA’s AI chips. The Gentlemen listed it on 6 October 2026 and claim more than 9TB of data. Jentech has not confirmed an incident that Ransomnews could find.
Who handles The Gentlemen’s negotiations over NVIDIA?
The Tox ID on the NVIDIA entry matches the one Check Point Research attributed to the group’s administrator, known as zeta88. Check Point says the same ID is shown on the leak site as a contact for affiliates and victims.
Has NVIDIA been breached before?
Yes. NVIDIA confirmed in March 2022 that an intruder took employee credentials and proprietary information. The Lapsus$ group claimed that attack.
How many of The Gentlemen’s claims are confirmed?
The Gentlemen have posted 1,107 listings in 2026, and Ransomnews has confirmed 91 attacks by the group this year from public sources. That is about one confirmed attack for every twelve listings.
Sources and further reading
- Ransomnews Ransomtracker, The Gentlemen operator profile, entries recorded on 6 October, 27 October and 18 November 2026
- Check Point Research, Thus Spoke…The Gentlemen, 13 May 2026
- Taipei Times, report on Jentech’s second-quarter revenue, 8 July 2026
- Jentech, NVIDIA AI Factory MGX ecosystem
- FPT, announcement of its partnership with NVIDIA, 23 April 2024
- NVIDIA, conference call notice for third-quarter results
- BleepingComputer, NVIDIA confirms data was stolen in recent cyberattack, 1 March 2022
- Technext24, report on the NVIDIA listing
- Dark Web Intelligence, alert on the FPT Software listing
- US Securities and Exchange Commission, cybersecurity incident disclosure guide
Reporting by the Ransomnews Research Team. Listing details are The Gentlemen’s own claims. Ransomnews viewed the leak site and did not open or download any data. No leak-site address or contact ID is published.
The Ransomnews Monthly
One email a month. Original leak-site data, victim census updates, and the findings that did not make the articles. No spam, unsubscribe any time.
Double opt-in. We store your email, signup time, and IP for consent records (GDPR Art. 7). See our privacy policy.