The administrator of RAMP, the Russian-language ransomware forum the FBI seized on 28 January 2026, ran its escrow service personally at a 5% cut, bought US network access by the day, and on 1 February 2024 offered LockBit the identity of the XSS forum’s administrator for 10 bitcoin, in writing. Nine months after the seizure he has not been charged or publicly named. This is what the forum’s own records say about him.
About this investigation. The research, analysis and confidence assessments below are mine. I reviewed a copy of the RAMP forum database that circulated in the underground after the seizure, the same material CloudSEK and other researchers have described and that forum members cross-checked against the seized site. Every quotation attributed to the operator is a dated message he typed, reproduced as written, with my translation beneath. Where I draw an inference rather than quote a record, I say so and give my confidence. I worked the same way I did on the 5socks.net history: records first, public reporting second, inference last and labelled. Nothing here identifies the operator by legal name, and I do not claim to know it. Ransomnews edited this piece for style and checked the quotations against the source material and the public reporting cited.
In brief
- RAMP’s
adminandStallmanaccounts were one operator, confirmed by a six-minute account switch on one server on 17 April 2023 and by his own public post of 1 July 2022. - He described his trade in his third week as buying US government network access, and he ran the forum’s escrow personally at a 5% cut.
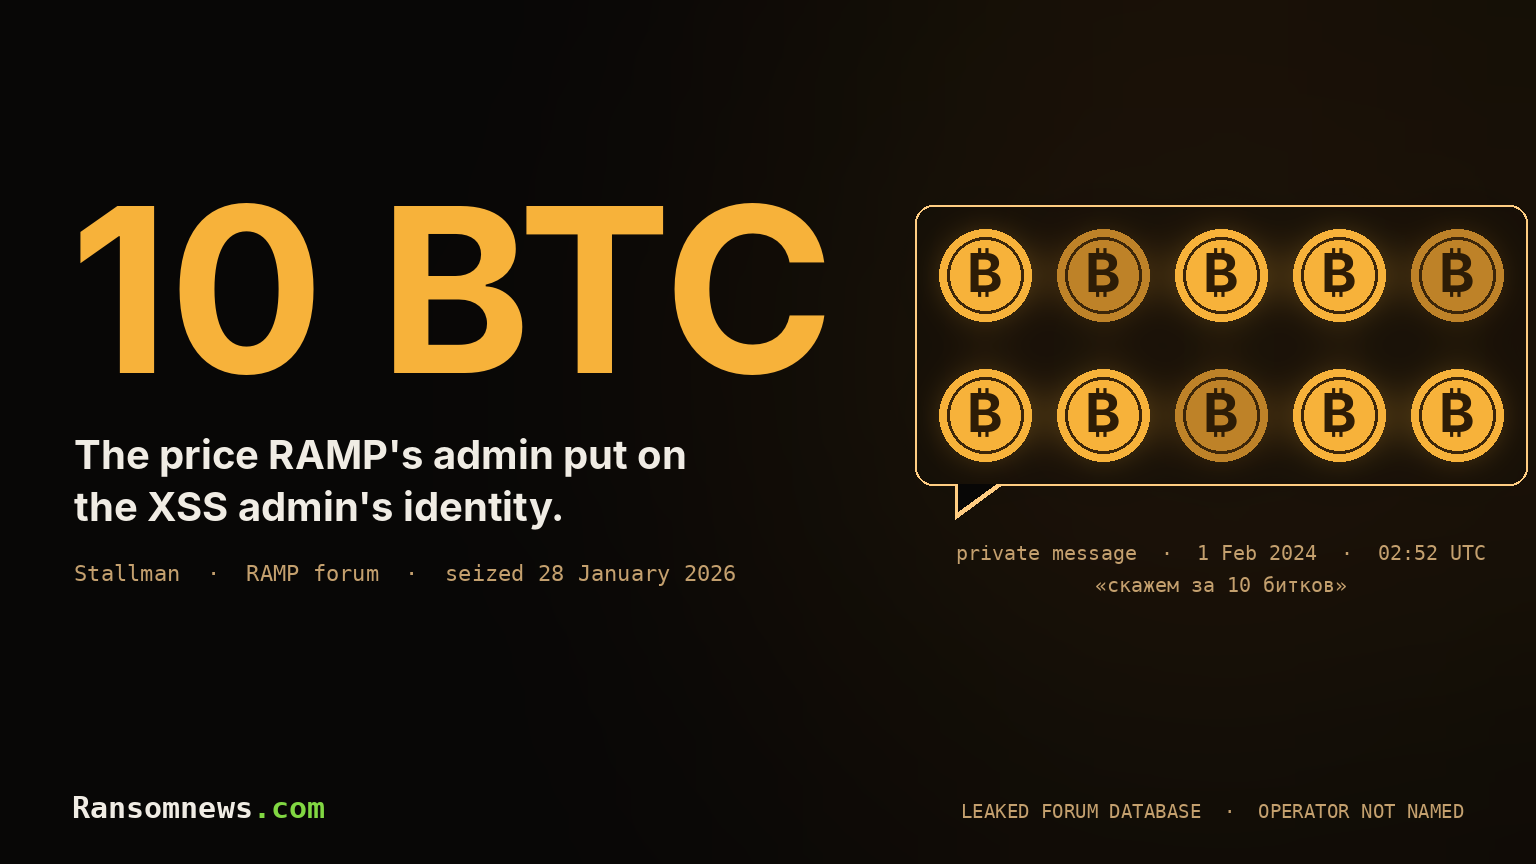
- On 1 February 2024 he offered LockBit’s operator the XSS administrator’s deanonymisation for 10 BTC, roughly $430,000 at the time, in a private message that survives verbatim.
- His escrow arithmetic matches the blockchain to the satoshi. His master wallet took in 55.84 BTC across 596 transactions, and on 2 January 2025 about 118 BTC moved through mixer-style transactions that included his addresses.
- Activity patterns put him in the UTC+2 to UTC+3 band. One Verizon Wireless mobile login is the only non-VPN connection in a year of logs.
- Whether he was also RAMP’s earlier administrator, Kajit, is open. I rate the single-operator reading at moderate confidence.
- As of October 2026 he has not been charged or named, and the FBI has said nothing about the seizure.
Who ran RAMP?
One operator ran RAMP through two accounts, a root account called admin and a public persona called Stallman, from the forum’s relaunch in late 2021 until the seizure. I rate that finding as confirmed.
RAMP opened to the public on 1 November 2021 under the slogan “the only place ransomware allowed”. Its account table holds the ownership story in two rows. The admin account was registered on 18 October 2021, two weeks before launch, with a placeholder email address. The Stallman account was registered in the forum’s first hour on launch day, with the address stallman2@thesecure.biz. Each account set a timezone that meant nothing, Europe/London for one and Atlantic/Reykjavik for the other.
| Field | admin | Stallman |
|---|---|---|
| Registered | 2021-10-18 14:45 UTC | 2021-11-01 23:33 UTC |
| placeholder | stallman2@thesecure.biz | |
| Staff groups | administrator | staff |
| Public posts | 70 to 75 | 5 |
| Private messages | 535 in hundreds of threads | 59 in 23 threads |
| Last activity | 2024-02-01 | 2023-04-17 |
On 1 July 2022, in a public post from the admin account, the operator said it himself:
«Теперь Я владелец и админ этого форума теперь, использую аккаунт @admin, Stallman»
Now I am the owner and admin of this forum; I use the account @admin. Stallman.
The login record says the same thing without words. On 17 April 2023, every event below came from the forum’s own management server, a DigitalOcean VPS:
21:47:30  admin     login
21:48:21  Stallman  login                 (51 seconds later)
21:49:27  Stallman  4 private messages sent
21:51:16  Stallman  avatar_delete
21:51:21  Stallman  account_details_edit
21:51:35  admin     login
21:52:57  admin     private message sent
Six minutes on one keyboard. He logged out of the root account, logged into the public one, answered four waiting correspondents with the same line, «привет, пиши мне на аккаунт @admin, сюда не захожу» (hi, write to me on the @admin account, I don’t come in here), deleted the avatar, edited the account details and went back to being admin. That session is the last thing the Stallman account ever did. He retired the public account that evening and never touched it again, which I take as a sign he was tidying up long before he had a reason to.
What was his business?
He was an initial access broker specialising in US government networks before he was a forum administrator, and he said so three weeks after launch.
On 22 November 2021, answering a seller who had asked what kind of access he wanted and why, the Stallman account wrote: «Если коротко, то моя ниша это гос. доступы США. У меня свой приватный криптолокер.» (In short, my niche is US government accesses. I have my own private cryptolocker.) He repeated the first half to another seller on 9 December: «Моя тема это гос. доступы сша.» The private-locker claim is his; I have no way to test it and treat it as a claim.
His standing advert, first posted on 10 November 2021 and reused for years from both accounts, opened «С радостью выкуплю Ваши доступы» (I will gladly buy out your accesses). The volume, in a private message of 7 March 2023: “I buy 10-20 access per day now.”
The forum’s escrow was his second business. It was announced on 25 November 2021 as “represented by me personally”, and the workflow survives in dozens of threads, arithmetic included. “0.17 + 5% = 0.1785”, he wrote to a buyer on 3 January 2022. “0.20582992 + 5% = 0.216121416 BTC”, on 13 January, under the boilerplate «Это кошелек для вашей сделки» (this is the wallet for your deal). Five points on every trade, paid to addresses he supplied. The blockchain section below shows what those exact numbers did on-chain.
His rules were consistent across four years. Jabber first, always. TOX only after five completed deals. No researchers: «Я не использую токс, только жабу… сорри, ресечеры заебали» (I don’t use TOX, only Jabber, sorry, researchers have worn me out). He verified counterparties by making them write to his accounts on the neighbouring boards, «Мой акк на экспе @Stallman» (my account on Exploit is @Stallman), and when the forum’s guarantees were questioned he pointed to a 1 BTC deposit he had placed on exploit.in. To a staffer he was paying, he described his funds in English: “My bitcoins is white as hell, btw, no need to clean it again.”
What did he offer LockBit?
On 1 February 2024 the admin account offered the operator of LockBit the deanonymisation of the XSS forum’s administrator for 10 bitcoin, roughly $430,000 at that week’s price. I have read a lot of forum private messages over the years, and I have not seen another one like it.
The context is a feud that was public at the time. In late January 2024 LockBit’s representative was banned from XSS, the forum at the top of the Russian-speaking supply chain, after an arbitration over whether he owed a broker a percentage of ransom settlements. KELA’s reporting from September 2025 records that the ban “reportedly led to several personal threats made by LockBit against ‘Toha’ and his family”, Toha being the handle the underground uses for the XSS administrator, and that RAMP members asked in 2024 why Stallman had not banned LockBit over it.
The private conversation, titled «надо поговорить» (we need to talk), was opened by the admin account on 31 January 2024. All times are UTC and the translations are mine.
| When | From | Message |
|---|---|---|
| 31 Jan, 21:05 | admin | «Привет, есть жаба у тебя? Мне тут начинают писать тоже, что нужно банить тебя. Давай попробуем с моей помощью решить вопрос с баном на дамаге, чтобы не терять столько накопленной репы и бренд твой.» Hi, do you have Jabber? People here are starting to write to me too that you need to be banned. Let’s try, with my help, to settle the ban on Damage [XSS], so you don’t lose all that accumulated reputation and your brand. |
| 31 Jan, 21:27 | LockBit | «привет, жабы нет и не будет, я свою позицию высказал в арбитраже, договора небыло, админ хсс это сам написал, по его указанию я платить процент никому не собираюсь…» Hi, no Jabber and there won’t be. I stated my position in the arbitration. There was no contract, the XSS admin wrote that himself, and on his instruction I’m not going to pay a percentage to anyone… |
| 31 Jan, 22:16 | LockBit | «у тебя случайно нет деанона админа хсс? могу купить» Do you happen to have the XSS admin’s deanon? I can buy it. |
| 1 Feb, 02:47 | admin | «Я могу помочь и стать посредником между тобой и Тохой, если ты станешь чуть чуть погибче. Дай токс, если нет жабы, давай попробуем как-то выйти из этой ситуации без нервов.» I can help and act as a mediator between you and Tokha, if you become a little more flexible. Give me TOX if you have no Jabber, let’s try to find a way out of this without nerves. |
| 1 Feb, 02:52 | admin | «Случайно есть, я могу дать инфу на него, если между нами, скажем за 10 битков. Только лучше сделать по другому, и договориться. Ты что-то заплатишь, он тебя разбанит, и будем дружить семьями.» As it happens, yes. I can give you info on him, if it stays between us, say for 10 bitcoins. But it’s better to do it differently and come to an agreement. You pay something, he unbans you, and we’ll be friends as families. |
Look at what was on offer. LockBit, freshly banned by the most powerful forum operator in the ecosystem, wanted that operator’s real identity badly enough to ask for it by name and price. The RAMP administrator answered with a number and a condition of secrecy, and then, in the same message, offered to mediate and suggested everyone “be friends as families”. I searched the whole database for «дружить семьями». It appears once, here.
Whether he actually held the information is unverifiable; the offer is the fact. LockBit did not reply. His last recorded activity on RAMP is timestamped 02:36 UTC on 1 February 2024, sixteen minutes before the offer. Eighteen days later Operation Cronos seized LockBit’s infrastructure, and in May 2024 the US and UK named its operator as Dmitry Khoroshev.
One more line shows whose company he kept. LockBit’s only public post on RAMP, dated 17 December 2023 and delivered after a rival affiliate programme exit-scammed, reads: «Выплаты на кошелек адверта были, есть и будут только в одной партнёрке.» (Payouts to the advertiser’s wallet were, are and will be in only one affiliate programme.) Six weeks later, the man who had been escrowing LockBit’s deals at five percent was pricing a dox for him.
Was Stallman also Kajit?
The public record says RAMP passed from a burned administrator called Kajit to a buyer called Stallman in January 2022. The forum’s own records turn that into a question, and I rate the single-operator reading at moderate confidence, no higher.
The public chain first. RAMP’s creator is Mikhail Matveev, the broker known as Orange, Wazawaka and BorisElcin, indicted in the United States in 2023 and reported arrested in Kaliningrad in November 2024. Interviewed by The Record’s Dmitry Smilyanets in August 2022, he said: “I have never been Kajit.” He described recruiting Kajit as a moderator and added, “That’s how the forum actually fell into the hands of Kajit.” On what came next: “The damage [XSS] forum administrator suggested to Kajit to transfer the forum to someone else, and as far as I know, Stallman got it.”
Kajit lasted about three months. KELA’s annual ransomware report for 2021 records LockBit accusing him of links to law enforcement, of collecting information on REvil before the January 2022 arrests and of leaking a BlackMatter admin-panel screenshot, and concludes that “following LockBit’s efforts, KAJIT was banned from XSS and Exploit and resigned from RAMP administration.” Orange Cyberdefense’s history of the Russian-language forums carries the counter-reading that any fair account must: that Matveev himself spread the informant rumours after he had given the forum away.
Now the forum’s records. I pulled every post and private message from both accounts, 674 dated texts and roughly 49,000 characters, into one file and read them in date order, which is the only way to see where the writing changes. The admin root account was registered on 18 October 2021, the day that contemporaneous monitoring presented at Group-IB’s CyberCrimeCon that December put Kajit’s appointment as administrator. Through December 2021 the account signed posts “KJ” and “meow”. After 28 January 2022 that register is gone and it never comes back.
Free tool
How does your own site score?
Run the same forty passive checks against your own domain: TLS and certificates, security headers, SPF and DMARC, cookies before consent, and what your stack quietly reveals. A grade out of 100 in about fifteen seconds.
No signup. Nothing installed. We only request what your site already serves publicly.
On 6 December 2021 the admin account wrote to a staffer: “I need ramp.systems – namecheap account. password wrong.” He was running a private Jabber server on a domain of his own. On 11 December, in two conversations on the same day, the same account handed out two addresses on that server. To one correspondent: «жабу скину stallman@ramp.systems которая» (I’ll give you the Jabber, stallman@ramp.systems). To another: “I just chage the jabber dude dm me here – kajit@ramp.systems … its my new private jabber. dont share pls”.
On 11 December 2021 the forum was still publicly Kajit’s. The ban had not happened and the “sale” was weeks away. Yet an account named stallman@ already existed on the operator’s own server, beside the one he called his new private Jabber. Add the Stallman forum account itself, registered on launch day, five weeks before Kajit’s fall began. The buyer’s name was sitting on the seller’s own server before there was a sale. I can think of two explanations and I cannot rule either out from the text: Kajit was preparing a handover to a chosen successor before anyone had advised him to sell, or the buyer and the seller were the same man.
The takeover was announced to correspondents in February 2022, in several versions. 2 February: “it’s the same Stallman here now”. 3 February: «Привет, да, теперь это мой аккаунт. начало этой беседы вы вели не со мной, и его больше нет, он забанен.» (Hi, yes, this is my account now. You started this conversation with someone else; he’s gone, he’s banned.) 7 February: «я полностью забрал форум, его больше нет» (I took the forum over completely, he’s gone). 10 February, to a correspondent who had not asked: «ну я не Каджит, надеюсь ты это понимаешь? Первый рамп писался не для меня.» (Well, I’m not Kajit, I hope you understand that? The first RAMP wasn’t written for me.) A later recruiting message says the forum «был выкуплен мной лично у прошлой администрации несколько месяцев назад» (was bought out by me personally from the previous administration several months ago). So it was a ban to one correspondent, a takeover to another and a purchase in his own advertising, depending on who was asking.
The staff never settled on one story either. A junior moderator, writing to the admin account on 17 May 2022, greets it as «Привет Стэлман» and in the same message recalls «мне Каджит заплатил 400 дол» (Kajit paid me 400 dollars). A member wrote to the account’s own TOX ID in August 2022: «Ник RED, он же KAJIT» (the nick RED, a.k.a. KAJIT). And on 22 April 2023, fifteen months after the handover, a staff member asked the admin account directly: “kajit, its u??” The reply preserved in the record deflects. It does not deny.
The case for two people is real and I give it its weight. The first-person purchase statements are explicit and repeated. The style break at the end of January 2022 is total: the flamboyant Kajit register disappears and never returns, which is as consistent with a new hand as with a deliberate change of mask by a man who had watched style analysis happen to other people. CloudSEK’s reading of the same material has a partner, “honey”, who also used the Khajit name, which gives the two-hand reading a second body; that partner’s account resurfaced in October 2023 to ask Stallman, “this is not k***t, this is his partner. we share this account, you know somethin about him? he disappeared about 5 aug”. Nobody has publicly answered that question.
Against the two-hand reading: the “two men” share verbal tics found from nobody else on the forum. «Давай сначала свою, иначе не добавлю, спаммеры заебали» (give me yours first or I won’t add you, the spammers have worn me out) appears from the Stallman account in early 2022 and from the admin account in September 2023, typo variants included, and from no third account in the entire database. The access buyer’s one-word «Поймал» (caught it), the English sign-off “Thank you for your service”, and the same schoolmaster’s reflex of correcting other people’s Russian (“what is your native language, bro? your russian is no good” from Stallman in 2021; «Пиши по английски, если русский не родной» from admin years later) all cross the boundary. So do the same spelling mistakes in both languages, the dropped soft signs and the doubled consonants, which are the kind of thing a writer does not notice about himself. And there is a motive: a persona accused by the biggest crew in the ecosystem of working for the police cannot run a trust business, and a staged sale to the forum’s own escrow man launders the name without surrendering the asset.
My assessment: moderate confidence that one hand ran RAMP from October 2021 to January 2026 under two names, Kajit and then Stallman. It is not provable from text and I do not claim it is. If there were two men, the second arrived with the first man’s private server, his vocabulary, his escrow wallet within days, and his staff’s unshaken suspicion. From February 2022 onward the question closes either way: admin and Stallman are one operator, and that operator is the man the FBI’s banner was addressed to.
A note on the handle. “Stallman” on a ransomware forum is almost certainly a free-software joke, and the name recurs in the underground. A “Stallman” who sold drops and card dumps on the Carder Pro board in 2012, in English, is a different trade and a different hand; I checked it and set it aside. More telling is the absence: none of the RAMP operator’s contact identifiers, his Jabber addresses, his TOX IDs, the ramp.systems domain, has ever surfaced on another forum or in any public index. His perimeter held against everyone in his own world.
Where did the money go?
His escrow and advertising businesses left twelve Bitcoin addresses in his own messages, every one of them real and swept empty, and the arithmetic in his private messages is reproduced on the public ledger to the satoshi. I used nothing more exotic than a public block explorer and WalletExplorer’s clustering for this part, so anyone can repeat it.
| Address | Role, per his messages | Lifetime received | Active |
|---|---|---|---|
1Bc4NkmoQb7a5eA1M2PCChFre8AcETyUBC | Master wallet | 55.844 BTC, 596 txs | 2021-04-05 to 2024-08-23 |
bc1q6j6g9j24cfkg57hrhz6yev9ym6pleuhtpekkgq | Escrow, most used | 0.39462142 BTC | Jan 2022 |
19g7mbR9d6uGUyFPewV1oMz28ciEFdhXQm | Escrow refund and payout | 0.13589597 BTC | 2022-01 to 2022-05 |
bc1qk3rh7c0h5pv02rluscjnyrce6kv0n5hv8neaxw | Banner ad sales | 0.10829661 BTC | 2022-03 to 2024-12 |
bc1qlkltuywcqs03wxu46elh6w2d5e0fvsdw4ddcfd | $200 vendor verification fee | 0.00736240 BTC | 2023-05 to 2024-12 |
Three bindings tie the typing to the ledger. First, the two escrow sums he quoted in January 2022, 0.1785 and 0.21612142 BTC, are exactly the only two deposits bc1q6j6g9j… ever received, 0.39462142 BTC in total, and the buyer in that thread posted a blockchain.com link confirming his payment into the same address. Second, a “verified transaction” he posted on 18 January 2022 as proof of a payout pays 0.13589597 BTC to his own refund address from an intermediate wallet that had been funded six minutes earlier by the spend of his main escrow address; one actor controlled all three points of that triangle. Third, the 7 January 2022 spend of the escrow address sent 0.06375 BTC in a single hop to 1Bc4Nkmo…, the master wallet. That wallet, 596 transactions and 55.84 BTC of lifetime throughput, was active from 5 April 2021, seven months before RAMP launched, so there is a pre-RAMP financial trail on-chain for this man. CloudSEK’s independent reading of the cluster counts $234,102 across 1,099 connected addresses, first active on 4 January 2022 and last active on 2 September 2025.
Both sides of the money touch a major exchange within one hop. Between July 2021 and May 2023 the master wallet made more than sixty round-amount payments, about 8.87 BTC in all, to two addresses that clustering tools attribute to a single high-volume service. That service’s periodic sweeps settle directly into an address publicly labelled by several chain-analytics sources as Binance’s hot wallet. On the inbound side, the master wallet’s two largest repeat funders, 4.035 BTC over 24 deposits and 2.525 BTC over 11, were themselves funded by withdrawals from the same hot wallet. I state this as flow and nothing more: there is no suggestion that the exchange did anything wrong, and the accounts on the far side may belong to intermediaries rather than to the operator. What it means is that an exchange holds customer records one hop from his money in both directions. Strong on the flows, which are public; moderate on whose accounts they are.
What he did with the coins afterwards says a lot about how exposed he thought he was. On 23 December 2024, between 17:56 and 18:45 UTC, all six dormant ad-sale and fee addresses were emptied into six fresh SegWit addresses within 49 minutes, which is also the final proof that the six fronts belonged to one operator. On 2 January 2025, inside a three-hour window, all six migration addresses entered four very large fan-out transactions, each with between 240 and 294 inputs and 274 and 347 outputs, carrying about 118 BTC in total. The outputs are structured in exact powers of two in satoshis and were later re-gathered in batches of a hundred or more inputs. Exactly one operator address appears in each fan-out; the other inputs belong to strangers. That pattern is what a commercial mixer or swap service leaves behind. The chain facts are confirmed; which service it was, I do not know, and I rate the mixer reading moderate. Note the timing: this ran eleven months after his last message on record and thirteen months before the FBI arrived.
Where was he?
Behaviourally, in the UTC+2 to UTC+3 band, Eastern Europe or European Russia, working a Moscow-time day. He confirmed the arithmetic himself twice without noticing. I rate the band at moderate confidence.
The record holds 1,568 dated events for the admin account across 2021 to 2024, including 808 hand-typed private messages. Aggregated by hour, the quiet window runs from roughly 04:00 to 10:00 UTC, and the Stallman account and a third, textless staff persona on the same infrastructure share it. The master wallet’s spend-hour histogram, an independent source, peaks between 05:00 and 15:00 UTC. He said it in words too. “got it, money on the way, could take up to 12 hours, it’s a night time here”, sent at 01:41 UTC on 11 October 2023, which is 04:41 in Moscow. And on 8 March 2023: “Today is a holiday in russia, so check tomorrow too.” He worked the forum seven days a week, often in runs of twelve UTC hours or more. The forum was his full-time job, not a side project.
His network discipline was close to total, with one exception. The forum’s IP records cover only the operator’s final year, February 2023 to February 2024, because the software pruned anything older. Within that year, 958 logged events for the admin account resolve to the DigitalOcean management VPS, server-internal Docker addresses, Tor, and six commercial VPN brands rotated by the month: Datacamp/CDN77 and Avast SecureLine exits in New York and Frankfurt, and a white-label consumer pool sold under city labels that do not match where the servers are. A textless staff persona on the same server used that same white-label vendor for nine months. No residential ISP address appears anywhere in the three accounts’ records.
Exactly one row does not fit. On 30 March 2023 at 12:14 UTC the admin account made a cookie login, a remembered browser session, from a Verizon Wireless mobile address in the Philadelphia area. It is the only non-VPN, non-server address the account used in 958 events. There are two honest readings. US mobile proxies are a standard product on the very forums he ran, and he had an observed habit of testing a new proxy source once and moving on. Or a phone on Verizon’s network, in the United States, opened a remembered session at eight in the morning Eastern. The carrier, the timestamp and the uniqueness are confirmed. Which reading is true, I cannot tell from outside, and I do not pretend to.
What happened after the seizure?
He said goodbye on XSS, promised to keep buying access, made one claim that was disproven within hours, and was banned from every major underground forum inside a week.
On 28 January 2026 RAMP’s Tor site and its clearnet domain were replaced with a seizure banner naming the FBI, the US Attorney’s Office for the Southern District of Florida and the Justice Department’s Computer Crime and Intellectual Property Section, with RAMP’s own slogan reproduced beneath it and a winking Masha from the Russian cartoon. DNS moved to the Bureau’s standard seized-domain nameservers. The FBI declined to comment to BleepingComputer and The Register, and it has stayed silent since. As of publication there is no press release, no unsealed indictment and no reward notice naming RAMP’s administrator; I checked again before this piece went up.
Within days he surfaced on XSS. In a post that The Register and others reproduced, he wrote that “this event destroyed years of my work to create the most free forum in the world”, that the risk was one “we all take”, that he could not start a new forum, and that “I will continue to buy accesses. My core business remains unchanged.” Nobody has arrested him, and on his own account he has not stopped.
Then he claimed the forum’s disks had been encrypted and that the circulating screenshots were fabrications. CloudSEK’s account of what followed: trusted intermediaries cross-verified private messages from RAMP against the seized material and they matched, and the claim was dead in an afternoon. Within hours, per the same reporting, members were writing that “information came in that he was an informant”. The theory had two pillars: his public friendship with Severa, a figure the underground widely regards as a US cooperator, about whom users recalled him writing “I know Severa, he knows me, I travel around Europe, still haven’t been caught”; and the seizing jurisdiction, the Southern District of Florida. Within a week he was banned from every major forum. Whether he was an informant, a scapegoat or simply the last man holding the bag, the record does not say, and I will not pretend it does.
Five months earlier he had been at the top of the ecosystem. After the XSS administrator was arrested in Kyiv on 22 July 2025, the relaunched XSS needed staff it could trust. KELA’s monitoring records that on 18 August 2025 its administration appointed Stallman as moderator of the sellers and breaches sections with the words “Stallman de facto leads ransomware community”, that he registered on the splinter forum DamageLib as “Stallman2” on 27 August, and that in the deposit crisis that followed the arrest he argued moderators’ deposits should be repaid first. If the single-operator reading above is right, this is the second time the same man has been burned as an informant, under a different name, by the same crowd.
The market re-formed in weeks. Flare’s Tammy Harper told The Register that removing a hub “does not eliminate the ecosystem” but “forces migration”, and groups including DragonForce moved to the successor board Rehub. The forum is gone; the trade it served carried on without it.
What would it take to name him?
The answer sits in records I cannot reach, not in more research. Everything that can be assembled from outside is above, and it stops one step short of a passport. That step sits in a short list of places: the seized RAMP server itself and whatever four years of an escrow business left on it; the exchange whose customers sit one hop from his money on both sides; the hosting provider that billed the management VPS for a year; the registrar that sold him ramp.systems in December 2021; the VPN vendors whose pools his accounts lived in; and the thesecure.biz Jabber service that hosted at least two of his addresses, which Europol says was operated by the man arrested in Kyiv and which, per a forum post reported by KrebsOnSecurity, went to police with two years of logs. Several of those are already in law-enforcement hands. None of them is mine to ask.
There is also a human lead, and I have deliberately not named him. The forum’s original builder, who wrote in February 2022 that “all the infrastructure (containers, networks, the backup system) was written by me” and that the old backup server had been “switched off for nonpayment”, left the team three weeks before the takeover was announced, on bad terms. He knows who paid the bills.
What this means for defenders
The man who ran the ransomware world’s most visible forum described himself, in week three, as an access broker whose niche was US government networks, and the seizure did not change that. The access-broker layer is where this record is most useful. He bought ten to twenty accesses a day, paid in Bitcoin through an escrow he controlled, and the supply he described in his own messages was weak credentials on exposed administrative interfaces, the kind of entry the site’s initial access broker analysis, linked above, covers in detail. Forum seizures remove the storefront. The buyers, as he told the underground himself, keep buying.
For researchers, the record is a standing instrument. The linguistic fingerprint, the rationed-contact rules, the escrow arithmetic, the wallet hygiene and the sleep window are all measurable, and any future account on any forum can be held against them. He said his core business was unchanged. The habits in this record are the ones to watch for.
The operator’s known contact channels are seized or dead. If he, or anyone acting for him, wants to respond to anything in this investigation, Ransomnews will publish what they say.
Frequently asked questions
Who is Stallman, the RAMP administrator?
Stallman is the handle of the operator who ran the RAMP ransomware forum from late 2021 until the FBI seized it on 28 January 2026, through a root account called admin and a public persona called Stallman. His legal name has not been published by any outlet, researcher or law-enforcement agency.
Has the RAMP admin been arrested or charged?
No. As of October 2026 the FBI has issued no statement on the seizure, and no indictment, press release or reward notice naming RAMP’s administrator has appeared. Within days of the seizure he posted on XSS that he would continue buying network access.
What did Stallman offer LockBit?
On 1 February 2024 the RAMP admin account told LockBit’s operator, in a private message, that he could provide information deanonymising the XSS forum’s administrator for 10 bitcoin, if it stayed between them. LockBit did not reply, and Operation Cronos took its infrastructure down eighteen days later.
Was Stallman the same person as Kajit?
Possibly, at moderate confidence. The public record describes a sale from Kajit to Stallman in January 2022, but the Stallman forum account and a stallman@ramp.systems Jabber address both existed on the operator’s own infrastructure weeks before the sale, and the two accounts share verbal tics found from nobody else on the forum. The two-person reading is also consistent with the record.
How much money passed through the RAMP admin’s wallets?
His master wallet received 55.84 BTC across 596 transactions between April 2021 and August 2024, with a dozen smaller escrow and advertising addresses feeding it. CloudSEK’s separate analysis of the escrow cluster traced about 234,000 dollars across 1,099 connected addresses between January 2022 and September 2025.
Where is the RAMP admin based?
Behavioural evidence places him in the UTC+2 to UTC+3 band, Eastern Europe or European Russia: his activity and his wallet’s spending share a Moscow-time sleep window, and he referred to “a night time here” at 04:41 Moscow time and to a Russian public holiday. His only non-VPN connection in a year of logs was a Verizon Wireless mobile address in the United States, which is consistent with either a mobile proxy or a phone.
Sources and further reading
- BleepingComputer: FBI seizes RAMP cybercrime forum used by ransomware gangs (28 January 2026)
- The Register: Ransomware crims forced to take off-RAMP as FBI seizes forum (28 January 2026)
- CloudSEK: The rise and fall of RAMP, inside the forum where ransomware was always welcome (2026)
- KELA: XSS forum after takedown, DamageLib emerges (4 September 2025)
- The Record: An interview with initial access broker Wazawaka (26 August 2022)
- Orange Cyberdefense: Russian-language cybercriminal forums, chapter II (January 2024)
- KrebsOnSecurity: Who got arrested in the raid on the XSS crime forum? (6 August 2025)
- CyberScoop: Authorities in Ukraine nab alleged admin of Russian-language cybercrime forum (July 2025)
- Ransomnews: XSS forum, from DaMaGeLaB to the 2025 takedown
- Ransomnews: LockBit 5.0, the comeback nobody wanted
- Ransomnews: 5socks.net, 20 years of proxy crime, 2004 to seizure
- Ransomnews threat-group catalogue
Contributor and legal notice. This article is an independent investigation by Dancho Danchev, a contributing writer, published under his byline. The research, source material, translations, analysis, confidence assessments and conclusions are the author’s own, and the opinions expressed are his and do not necessarily represent the views of Ransomnews, its editors or its publisher, Greywatch IT Ltd. The author is responsible for the accuracy of the material he supplied. Quotations are reproduced from a copy of the RAMP forum database that circulated after the January 2026 seizure; Ransomnews makes no representation about the origin of that material. Nothing in this article identifies the RAMP administrator by legal name or claims to. References to named individuals reflect public statements by law-enforcement agencies, courts, researchers or the individuals themselves, as cited, and every person referred to is presumed innocent unless and until convicted by a court. Cryptocurrency addresses and transaction identifiers are public blockchain data reproduced for verification. Where the article states an inference rather than a record, it is labelled as the author’s assessment with his confidence level. If you believe anything here is inaccurate or unfair, or you are referred to in it and wish to respond, write to [email protected]; corrections and responses will be published.
The Ransomnews Monthly
One email a month. Original leak-site data, victim census updates, and the findings that did not make the articles. No spam, unsubscribe any time.
Double opt-in. We store your email, signup time, and IP for consent records (GDPR Art. 7). See our privacy policy.