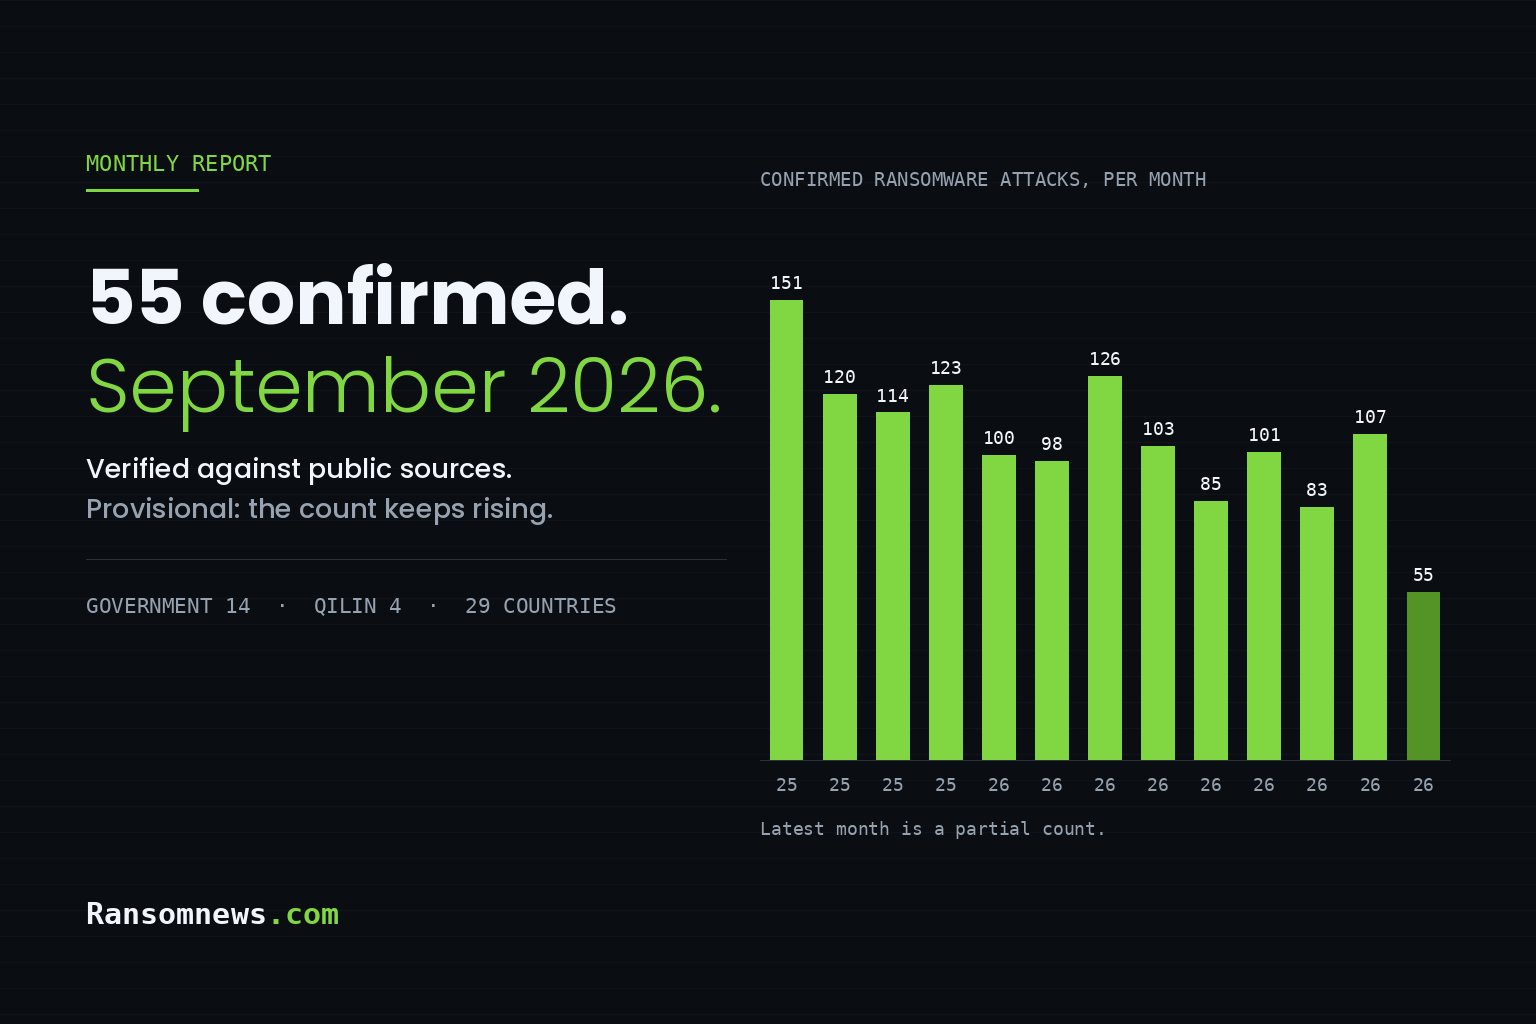
Ransomnews has confirmed 55 ransomware attacks in September 2026, against 107 in August 2026 and 151 in September 2025. The figure is provisional: September closed recently, and confirmed counts keep climbing for months after a month ends, so this total will rise. Government bodies led the sectors with 14 incidents, and Qilin and The Gentlemen each had four confirmed victims.
The count, and why it will rise
Every row behind this report is an incident verified against a public source, which means a month only fills in as organisations issue statements, regulators publish notifications and local outlets pick up the story. Over the twelve months to August 2026 the confirmed table averaged about 109 incidents a month, and a month’s figure typically keeps rising for three to four months after it ends. September’s 55 should therefore be read as a floor, not a total, and the gap with August’s 107 is mostly a reporting lag rather than a measured drop in activity.
The live September 2026 page carries the full incident list with a source link for every entry, and it updates as new disclosures are verified. For the wider year, 859 incidents are confirmed across 2026 so far, against 1,128 over the same January to September window in 2025.
Which groups had the most confirmed victims
Of the 55 confirmed incidents, 38 carry an attributed group, so roughly a third are recorded without one. Qilin and The Gentlemen tied at the top with four confirmed victims each. Dire Wolf, Rhysida and INC each had three, and SETTRA, LockBit and Kairos each had two. The counts are small enough that one late disclosure can reorder the table, and attribution usually rests on a leak-site listing or on the victim naming the group, so the shape of the month matters more than the ranking.
Sectors and countries
Government was the most affected sector with 14 incidents, followed by healthcare with 11 and education with eight. Technology recorded five, retail four, transportation three, and services and manufacturing two each. Public bodies and hospitals are over-represented in confirmed data partly because they are obliged to tell people when services stop.
Incidents came from 29 countries. The United States led with 12, then Japan with six, Germany with five and Australia with three, with France, Spain, Italy and South Africa on two each. That distribution reflects disclosure rules as much as targeting: US breach-notification law pushes more incidents onto the public record than most other jurisdictions do.
Free tool
How does your own site score?
Run the same forty passive checks against your own domain: TLS and certificates, security headers, SPF and DMARC, cookies before consent, and what your stack quietly reveals. A grade out of 100 in about fifteen seconds.
No signup. Nothing installed. We only request what your site already serves publicly.
Notable confirmed incidents
- Air Traffic and Navigation Services, Gauteng, South Africa, government, group not attributed. Source
- Namibian Defence Force, Windhoek, Namibia, government, attributed to RansomHouse. Source
- Tottori Prefecture environmental radiation monitoring system, Tottori, Japan, government, group not attributed. Source
- Poder Judicial de la Provincia de Jujuy, Jujuy, Argentina, government, attributed to EMPERADOR. Source
- Mississippi Institutions of Higher Learning, Mississippi, United States, government, group not attributed. Source
- Springfield Public Schools, Massachusetts, United States, education, attributed to Interlock. Source
- DFI Retail Group, Quarry Bay, Hong Kong, retail, attributed to SETTRA. Source
- Data Hub, Kathmandu, Nepal, technology, group not attributed, with stock market trading halted. Source
Springfield Public Schools is also the month’s largest confirmed incident by records, at about 10,000. It is the only September row so far with a records figure attached, which is normal this early: record counts tend to surface in regulator filings weeks or months after the attack itself.
Ransom outcomes
No September 2026 row records a ransom payment, and eight record a refusal. The remaining 47 are unknown, which is the usual outcome: most victims never say either way, and the ones who do speak are disproportionately those who refused and recovered from backups. The confirmed figures therefore describe what organisations have disclosed, not how often ransoms are actually paid. Our payment-rate analysis sets out how far the public record can be pushed on this question.
Frequently asked questions
How many ransomware attacks were confirmed in September 2026?
Ransomnews has confirmed 55 ransomware attacks in September 2026, each verified against a public source. The figure is provisional and will rise as further disclosures are verified.
Which ransomware group was most active in September 2026?
Qilin and The Gentlemen tied on four confirmed victims each. Dire Wolf, Rhysida and INC had three each. Of the 55 incidents, 38 carry an attributed group.
Which industry was hit most in September 2026?
Government, with 14 confirmed incidents, ahead of healthcare on 11 and education on eight.
Is the September 2026 figure final?
No. A month’s confirmed count typically keeps rising for three to four months after it ends, as statements, regulator notifications and local reporting arrive. Treat 55 as a floor.
Sources and further reading
- Ransomware attacks, September 2026, the live incident list with sources
- Ransomware attacks, 2026, the year to date
- Ransomware statistics
- Ransomware payment rate
- Confirmed ransomware attacks hub
The Ransomnews Monthly
One email a month. Original leak-site data, victim census updates, and the findings that did not make the articles. No spam, unsubscribe any time.
Double opt-in. We store your email, signup time, and IP for consent records (GDPR Art. 7). See our privacy policy.