Tracking the criminal infrastructure of the internet.
Ransomware operators, breach economics, threat-actor profiles, and the open-source investigation toolkit that makes it all visible. Updated daily.
Latest stories
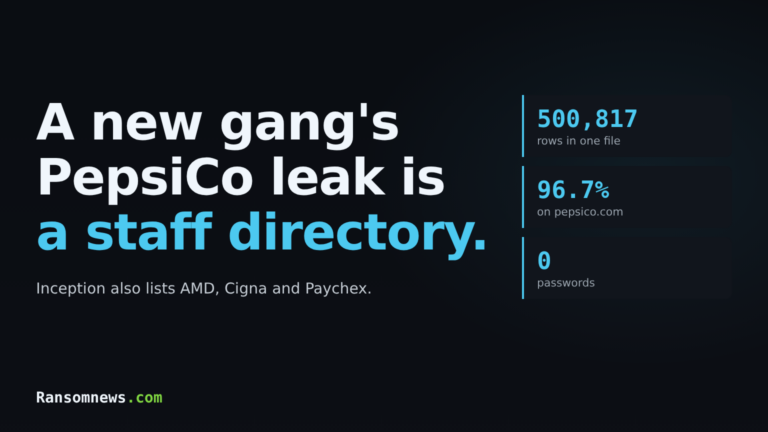
- Inception leaks PepsiCo staff directory, lists AMD and Cigna
 New extortion brand Inception named AMD, Cigna, Henry Schein, Paychex and PepsiCo on 17 November 2026. Its Cigna file holds 421,661 IT service desk tickets.
- n0n lists Eli Lilly, Visa and JPMorgan: no breach confirmedExtortion group n0n named 59 organisations on 16 November 2026, including Eli Lilly, Visa, Mastercard and JPMorgan Chase. None has confirmed a breach.
- Chase and Bank of America outage: was it a cyberattack?Chase, Bank of America, Wells Fargo and U.S. Bank customers reported outages on 16 November 2026. Chase says it is a technical issue, not a cyberattack.
- Old Bitly links hijacked in Burger King, McDonald’s and Trump tweetsBurger King and McDonald’s were not hacked. Someone re-registered the Bitly links in their 2011 tweets, and 57 of 97 links in old Trump tweets have been replaced too.
FOCUS
Ransomware
The defining cybercrime of the decade. How it works, who runs it, and where the money goes.
- Inception leaks PepsiCo staff directory, lists AMD and CignaNew extortion brand Inception named AMD, Cigna, Henry Schein, Paychex and PepsiCo on 17 November 2026. Its Cigna file holds 421,661 IT service desk tickets.
- n0n lists Eli Lilly, Visa and JPMorgan: no breach confirmedExtortion group n0n named 59 organisations on 16 November 2026, including Eli Lilly, Visa, Mastercard and JPMorgan Chase. None has confirmed a breach.
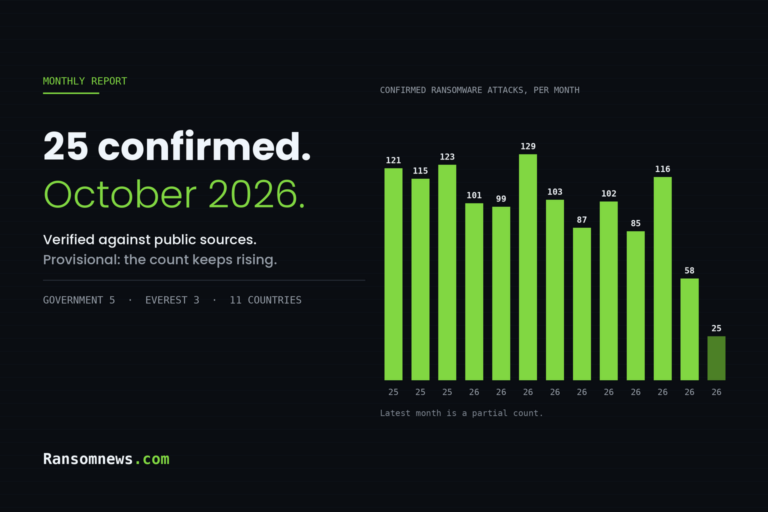
- Confirmed ransomware attacks, October 2026: 25 verified so far, Everest and The Gentlemen lead
 Ransomnews has confirmed 25 ransomware attacks for October 2026 so far. Everest and The Gentlemen lead with three victims each, government is the most-hit sector, and in 11 of 19 listed cases the gang went public before the victim.
PROFILES
Threat Groups
From LockBit and Conti to Akira and Cl0p, anatomies of the operations behind the headlines.
- Medusa ransomware: victims, tactics, and how to defend in 2026Medusa is a ransomware-as-a-service crew active since 2021, with 300+ claimed victims and 161 confirmed by Ransomnews. Its targets, tactics, biggest breaches and the defences that stop it.
- Interlock: the drive-by ransomware crew CISA flaggedInterlock breaks the ransomware playbook, entering through compromised websites and fake CAPTCHAs. A joint CISA-FBI advisory mapped its TTPs. Here is the profile.
- SafePay: the centralised crew that skipped affiliatesSafePay went from unknown to one of the busiest ransomware crews in under a year by ditching affiliates and hammering RDP and VPN gateways. Here is how it works.

DEFENCE
Security
EDR, Zero Trust, MFA, patching, IR, what actually works against modern threats.
- Chase and Bank of America outage: was it a cyberattack?Chase, Bank of America, Wells Fargo and U.S. Bank customers reported outages on 16 November 2026. Chase says it is a technical issue, not a cyberattack.
- Old Bitly links hijacked in Burger King, McDonald’s and Trump tweetsBurger King and McDonald’s were not hacked. Someone re-registered the Bitly links in their 2011 tweets, and 57 of 97 links in old Trump tweets have been replaced too.
- Microsoft 365 outage: was it a cyberattack? What we knowThe Microsoft 365 outage of 12 to 13 November 2026 was not a cyberattack. Microsoft blames a network capacity upgrade. What happened and what to do now.
SURVEILLANCE
Privacy
GDPR, data brokers, encryption, fingerprinting, VPNs, the surveillance economy and its limits.
- Codename Morgan: inside Morocco’s Pegasus machineForbidden Stories names Morocco as NSO’s client “Morgan”: a 2017 Rabat demo, an Emirati broker, roughly 12,000 targets, and Pegasus traces on seven French ministers’ phones.
- Inside Pegasus: NSO’s own files reveal the machineUnsealed NSO Group court files, analysed by Amnesty’s Security Lab and Forbidden Stories, expose how Pegasus really works: a vendor-run spyware service, not a weapon sold and forgotten.
- Stealer logs bypassing MFA in 2026 [Field Guide]Multi-factor authentication was supposed to end the credential-theft era. In 2026, it hasn’t, because adversaries skip the credential entirely and steal the session cookie that the authentication produced. Here’s how the attack works, why MFA doesn’t stop it, and the four controls that do.
MACHINE LEARNING
AI
Prompt injection, deepfakes, model theft, the EU AI Act, security and policy at the frontier.
- 36,769 exposed AI endpoints, only 2% ask for a loginMysterium VPN counted 36,769 self-hosted AI endpoints reachable on the public internet. Only 2.02% return an authentication challenge, and that is a floor.
- What is slopsquatting? AI package hallucinations, explainedSlopsquatting is a supply-chain attack that weaponises the package names AI coding assistants invent. How it works, what the research measured, the real 2026 incidents, and how to defend an AI-assisted pipeline.
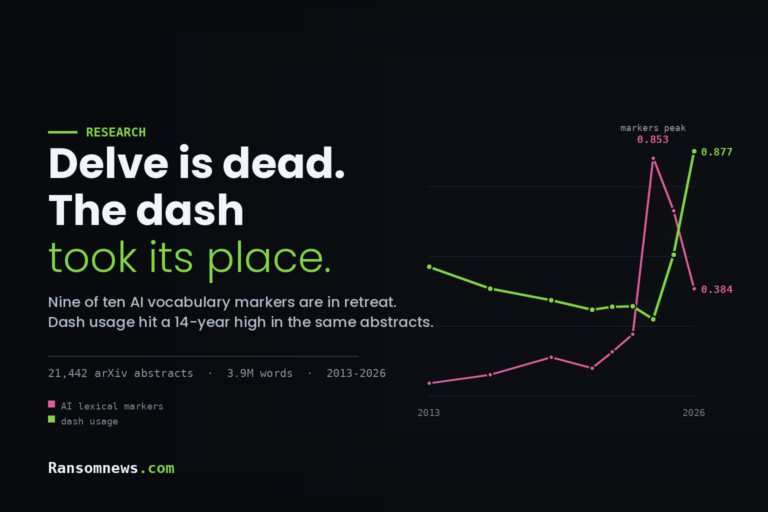
- “Delve” is dead: AI writing tells expire in 18 monthsThe word delve fell 94% from its 2024 peak while dash use doubled. We measured 21,442 arXiv abstracts: AI writing tells expire in about 18 months.

INVESTIGATIONS
OSINT
Tools, methods, and case studies from the open-source investigation discipline.
- Best OSINT tools 2026: what analysts actually runThe OSINT tools worth your time in 2026: Maltego, Shodan, SecurityTrails, DarkOwl, theHarvester and more, ranked by what they do and what they leak.
- Maltego tutorial: OSINT link analysis in 2026A hands-on 2026 guide to Maltego for OSINT: entities, transforms, machines and how to build a corroborated link chart from a single selector using the free Community Edition.
- GraphSense tutorial: open-source crypto tracing in 2026A hands-on 2026 guide to GraphSense, the open-source cryptoasset forensics platform: address clustering, TagPacks and how to trace ransom funds without a paid licence.
PRIMERS
Explainers
Long-form primers on the underlying concepts. Built to be referenced, not skimmed.
- What is intermittent encryption? A 2026 guideIntermittent encryption locks only parts of each file so ransomware runs faster and hides from detection. Here is how partial encryption works and how to catch it.
- What is RaaS? Ransomware-as-a-service, explainedRansomware-as-a-service splits ransomware into a rented product and an affiliate workforce. Here is how the RaaS model works and why it made attacks scale in 2026.
- What is BYOVD? Bring your own vulnerable driver, explainedBYOVD lets attackers load a legitimate but vulnerable signed driver to kill EDR from the kernel. Here is how it works and why ransomware crews rely on it in 2026.