THE TRACKER
Ransomtracker
A continuously updated index of ransomware leak sites: every victim listing as the operators publish it, who posted it and when. Built to make the leak-site economy visible, searchable and citable.
As of 22 November 2026 (UTC), Ransomtracker lists 16 victims published in the last 24 hours, 955 so far this month and 10,106 in 2026, with 74 ransomware operations posting in the last 30 days out of 651 catalogued. Most active over the last 30 days: N0N (244), The Gentlemen (123), Qilin (84). Every entry is an operator claim from a leak site, indexed as published and never verified by Ransomnews.
Live index · newest listing 2h ago · figures recalculated 44m ago
TRENDS
How is the leak-site economy moving?
Two years of monthly volume by operator, the year’s leaderboard, how many leak sites appear and disappear each quarter, and the hours and days when listings go up. Every chart is drawn from the live index and the numbers are in the page, not in an image.
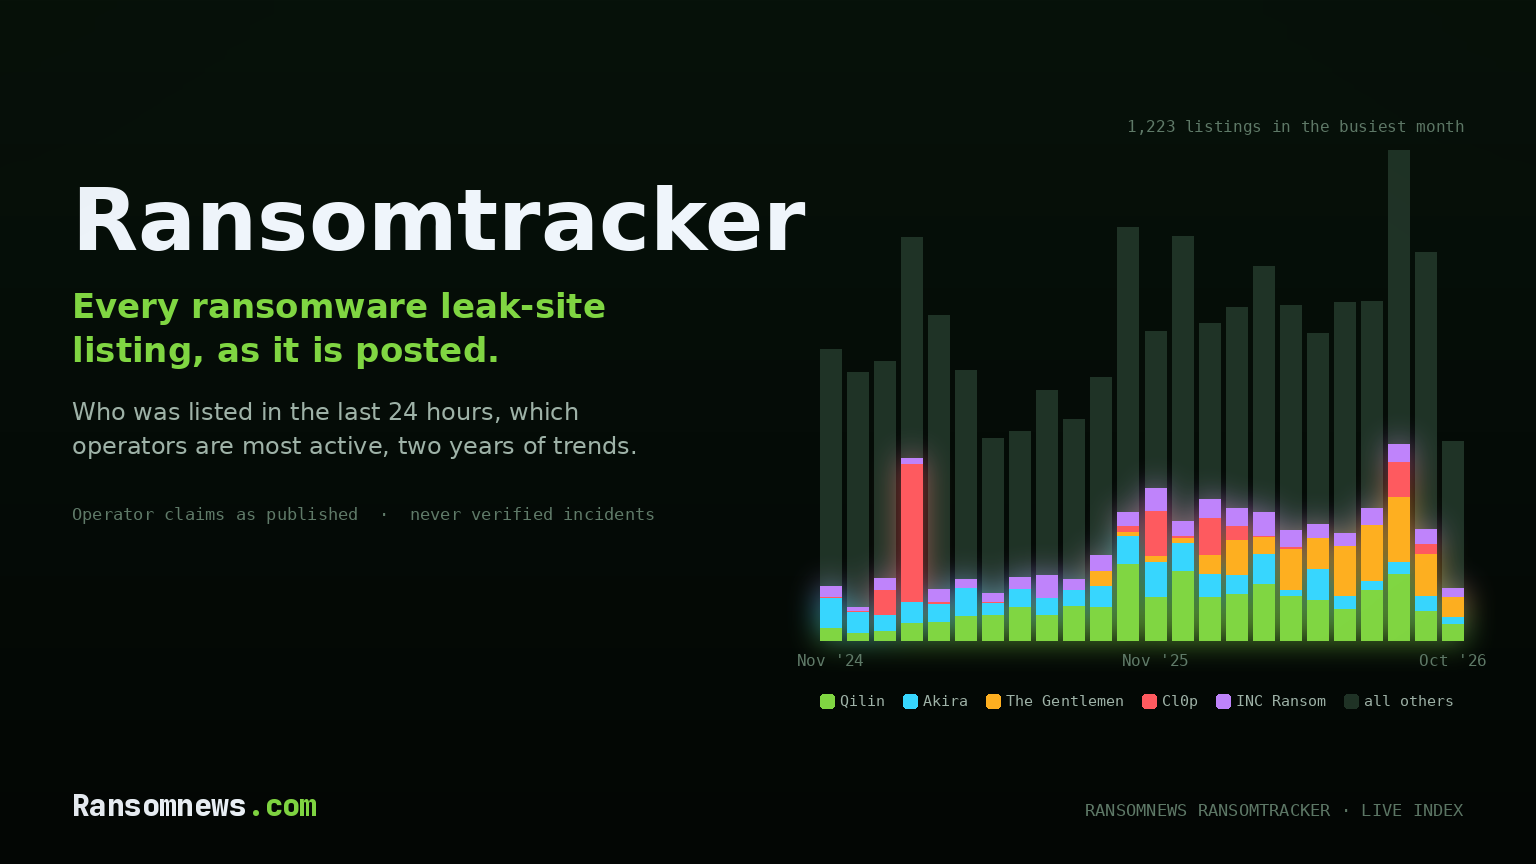
Victims listed per month
Last 24 months, Dec 24 to Nov 26, stacked by the five operators with the most listings in the window. The current month is partial and shown lighter.
Most active operators, 2026
Victims listed year to date.
Operator churn by quarter
Leak sites posting for the first time versus sites that have stopped. A site counts as dark after 90 days without a listing, so the last two quarters can only rise.
When listings go up
Listings by weekday and hour, UTC, trailing 12 months. Darker cells are busier.
MAP
Where are the claimed victims?
Listings from the last twelve months by the victim’s country, where the operator’s own post, the victim’s domain or a recognisable city gave it away. Hover a country for the count.
Top countries, 12 months
Click a country, on the map or here, to browse its listings.
- United States1,402
- Germany280
- Canada187
- Italy186
- Brazil136
- United Kingdom134
- France127
- India117
- Spain90
- Australia89
- Japan80
- Mexico73
A country could be identified for 40.5% of the 11,113 listings in this window, from the operator's own description, the victim's domain or a recognisable city. The remaining 6,610 name no location and are not on the map. Leak-site posts skew towards operators who write descriptions, so treat this as a floor, not a census.
OPERATORS
Which ransomware groups are most active right now?
The fifteen operators with the most victim listings in the last 30 days, with the change against the previous 30 days, an eight-week trend and leak-site status.
| # | Operator | Last 30 days | Prior 30 | Change | Last listing |
|---|---|---|---|---|---|
| 1 · | N0N | 244 | 143 | +101 | 1d ago |
| 2 · | The Gentlemen | 123 | 125 | −2 | 3d ago |
| 3 · | Qilin | 84 | 102 | −18 | 22h ago |
| 4 ▲1 | INC Ransom | 61 | 36 | +25 | 22h ago |
| 5 new | Vortex | 42 | 0 | +42 | 1d ago |
| 6 new | Pixelleaks | 35 | 0 | +35 | 22h ago |
| 7 · | Akira | 33 | 32 | +1 | 1d ago |
| 8 ▲14 | Booba Team | 32 | 13 | +19 | 4d ago |
| 9 ▲5 | Leakeddata | 30 | 20 | +10 | 1d ago |
| 10 · | SafePay | 29 | 25 | +4 | 22h ago |
| 11 new | Soul | 28 | 0 | +28 | 22h ago |
| 12 ▲8 | Rhysida | 27 | 14 | +13 | 1d ago |
| 13 ▲34 | Whitearmor | 25 | 5 | +20 | 22h ago |
| 14 ▼2 | Everest | 20 | 24 | −4 | 1d ago |
| 15 new | Climax | 19 | 0 | +19 | 1d ago |
Ranked by victims listed in the last 30 days; change is against the 30 days before that. Status: live, a listing within 30 days · dormant, 30 to 180 days · dark, nothing for 180 days. Operator names link to full profiles with victim history and leak-site status.
SEARCH
Find a gang or victim
Searches active threat groups, victims listed across the trailing two years and, for a domain, infostealer-log exposure and affected services.
BROWSE
Browse the index
Every listing by year, filtered by operator or searched by name. Newest first.
| Date | Victim | Operator | Country |
|---|---|---|---|
| 22 Nov 2026 | UCA General Insurance Services, Inc | Endzone | not stated |
| 22 Nov 2026 | Invicta Watch Group | Qilin | not stated |
| 22 Nov 2026 | Data Breach at O&M University in the Dominican Republic | Hyflock | Dominican Republic |
| 22 Nov 2026 | Queens Public Library | The Gentlemen | United States |
| 21 Nov 2026 | ION Asset Architecture UK LTD | Qilin | not stated |
| 21 Nov 2026 | tiic.com.ph | SafePay | Philippines |
| 21 Nov 2026 | threeroyal.com | SafePay | not stated |
| 21 Nov 2026 | factotal.com | SafePay | not stated |
| 21 Nov 2026 | offshore-ocs.com | SafePay | not stated |
| 21 Nov 2026 | relax.es | SafePay | Spain |
| 21 Nov 2026 | pacifico.com.ar | SafePay | Argentina |
| 21 Nov 2026 | qrc-solutions.com | SafePay | not stated |
| 21 Nov 2026 | santak.com.sg | SafePay | Singapore |
| 21 Nov 2026 | themedical.co.il | SafePay | Israel |
| 21 Nov 2026 | Regions Behavioral Hospital | INC Ransom | not stated |
| 21 Nov 2026 | County government within a U.S. state | Soul | United States |
| 21 Nov 2026 | genica.com.ve | LockBit 5 | Venezuela |
| 21 Nov 2026 | Vegely Welding Inc. | Pear | not stated |
| 21 Nov 2026 | Law Office of Ronald D. Weiss, P.C | Pear | not stated |
| 21 Nov 2026 | Realta Technologies | Eclipse | not stated |
| 21 Nov 2026 | MT5 algo-trading farm (OneFunded funded account, WINSERVER) | Pixelleaks | China |
| 21 Nov 2026 | Lucid Motors | Inception | not stated |
| 21 Nov 2026 | DROP 1 — CASANARE, PAJONAL, PUTUMAYO AND URUS — 8,000 PATIENTS, 4,000 INVOICES, 7,733 CRED | Whitearmor | Colombia |
| 20 Nov 2026 | bastion.internal domain controller (GCP, GRATEFUL-V1) | Pixelleaks | United States |
| 20 Nov 2026 | Aixia Group AB (Nasdaq-listed AI/IT, Sweden) | Pixelleaks | Sweden |
Operator claims as published on leak sites, newest first; filter by year, operator or country, or search a name. Country is a best-effort reading of the listing, so a country filter shows the placeable listings only. Figures and rows come from the Ransomnews index of leak-site listings (source data: RansomLook, CC BY 4.0, adapted). Per-operator history, mirrors and status live on each operator's profile.
LAST 24 HOURS
Who was listed in the last 24 hours?
The newest victim listings across every tracked leak site, exactly as the operators posted them. Click an operator to open its profile; the daily digest carries the same list with yesterday, the seven-day average and a 14-day trend.
| Listed | Victim | Operator | Country |
|---|---|---|---|
| 2h ago | Invicta Watch Group | Qilin | not stated |
| 2h ago | Data Breach at O&M University in the Dominican Republic | Hyflock | Dominican Republic |
| 2h ago | Queens Public Library | The Gentlemen | United States |
| 13h ago | ION Asset Architecture UK LTD | Qilin | not stated |
| 15h ago | tiic.com.ph | SafePay | Philippines |
| 15h ago | threeroyal.com | SafePay | not stated |
| 15h ago | factotal.com | SafePay | not stated |
| 15h ago | offshore-ocs.com | SafePay | not stated |
| 15h ago | relax.es | SafePay | Spain |
| 15h ago | pacifico.com.ar | SafePay | Argentina |
| 15h ago | qrc-solutions.com | SafePay | not stated |
| 15h ago | santak.com.sg | SafePay | Singapore |
| 15h ago | themedical.co.il | SafePay | Israel |
| 16h ago | Regions Behavioral Hospital | INC Ransom | United States |
| 17h ago | County government within a U.S. state | Soul | United States |
| 22h ago | genica.com.ve | LockBit 5 | Venezuela |
Listings published in the last 24 hours, newest first. Country is only given where the operator stated one, a domain gave it away or a city could be matched; masked names are shown as the operator posted them.
METHODOLOGY
What the tracker tracks, and what it doesn’t
Ransomtracker is a continuously updated index of ransomware leak sites. The collector watches the public leak sites of every active operator it can reach, most of them Tor hidden services, parses each new victim listing the operators publish, normalises the data and keeps a structured record: the organisation named, the operator that named it, the time the listing was found and whatever description the operator attached. The page you are reading reflects the current state of that index, recalculated every fifteen minutes.
The index is built for journalism, threat intelligence and breach-response work. It is not a credential-leak service and it does not host stolen data, only the metadata of who appeared on whose leak site, when. Ransomnews separately maintains a human-verified dataset of confirmed ransomware attacks, corroborated against breach notifications, regulatory filings and press reports; the two are kept apart on purpose, because a leak-site claim and a confirmed incident are different things.
What we track
- Operators with publicly visible leak sites, typically 60 to 90 posting in any 30-day window, out of several hundred catalogued since 2022.
- Each victim listing the operator publishes: organisation name, listing time, and the description or demands the operator attached.
- Operator status, derived from activity: live (a listing within 30 days), dormant (30 to 180 days) or dark (nothing for 180 days).
- Aggregates: per operator, per month, per quarter and, where a country can be identified, per country.
What we do not track
- The leaked data itself. The tracker indexes that a victim was listed and by whom, never the stolen files. Hosting that data is illegal in most jurisdictions and unethical in all of them.
- Private negotiations, ransom amounts or confidential incident details. The tracker only sees what operators choose to publish.
- Groups operating without a public leak site. Pure-encryption operators, double-extortion holdouts who never publish, and small bespoke campaigns are invisible to leak-site monitoring by design.
Data caveats
- Victim listings are operator claims. Some are inflated, some are duplicated across rebrands, a few are fabricated, and some operators publish placeholder or masked names. The tracker presents them as the operator presents them and labels masked names; verifying any specific listing is the analyst’s responsibility.
- Country is a best-effort reading of the operator’s own text and the victim’s domain. Roughly a third of listings carry enough to place them; the rest are counted but not mapped.
- Leak sites change layout frequently and disappear without warning. Brief gaps in coverage for individual operators are expected, and a site that stops posting may be seized, retired, exit-scammed or simply unreachable.
- Attribution between rebranded operations (Conti to Black Basta, Royal to BlackSuit, and so on) is annotated on operator profiles where the lineage is well established and left ambiguous where it isn’t.
Source data: RansomLook (CC BY 4.0), aggregated, enriched and adapted by Ransomnews. Summary figures are available as JSON at /wp-json/rn-tracker/v1/stats, every listing of a year as CSV at /wp-json/rn-tracker/v1/export/year/2026.csv and a monthly summary since 2022 at /wp-json/rn-tracker/v1/export/monthly.csv; each year has its own archive page (2026, 2025, 2024, 2023, 2022) and the last 24 hours have a daily digest. Cite as Ransomnews Ransomtracker, with a link to this page.
FAQ
Frequently asked questions
What is a ransomware leak site?
A ransomware leak site is a dark-web page, usually a Tor hidden service, where a ransomware operator publishes the names of victims who have not paid, together with samples or full dumps of the stolen data. Ransomtracker indexes these listings, the fact that a victim was named and by which operator, never the stolen data itself.
How many ransomware groups are active right now?
Between 60 and 90 operators publish on a leak site in a typical 30-day window; the live figure is in the strip at the top of this page. Ransomtracker has catalogued several hundred operations since 2022 and marks each as live, dormant or dark from its posting activity.
Are the victim listings verified?
No. The listings are operator claims, shown as the operators publish them; some are inflated, duplicated across rebrands or fabricated, and some names are masked. Ransomnews keeps a separate, human-verified dataset of confirmed ransomware attacks, corroborated against breach notifications, regulatory filings and press reports.
How often is the tracker updated?
Continuously. The collector parses new victim listings as operators publish them; the counters, tables and charts on this page are recalculated every fifteen minutes from the live index.
Can I search Ransomtracker for a specific company?
Yes. Use the search box to check whether an organisation has been listed on a leak site, by which operator and when, or filter the index by year and operator. It is useful for due-diligence, breach-notification and threat-intelligence work.
Which country has the most ransomware victims?
The United States, by a wide margin, in every year the tracker covers; Germany, Italy, Canada, Brazil, the United Kingdom and France follow. The map on this page shows the last twelve months and states what share of listings could be placed in a country.
LEGAL & ETHICAL
A note on what this is for
Ransomtracker exists to make the operations of an entrenched criminal economy visible. The information it surfaces, that a particular organisation appeared on a particular operator’s leak site at a particular time, is already public, published by the operators themselves on indexed Tor sites, and widely scraped by other research, threat-intelligence and journalism projects.
The tracker indexes that public information. It does not host stolen data, does not assist in pressuring victims, and does not operate as a back-channel for any operator. If you are an organisation listed on the tracker and would like to share a public response or correction, write to editor@ransomnews.com. Corrections to operator metadata, story leads and sensitive tips go to the same address; we act on every submission.